Organisations across Europe are accelerating their migration to cloud infrastructure, yet this digital transformation introduces complex security challenges that traditional on-premises defences cannot adequately address. Cloud based security services have emerged as the essential framework for protecting business-critical data, applications, and workflows in distributed environments. Furthermore, these services provide comprehensive protection that adapts to evolving threats whilst ensuring compliance with stringent European regulations such as GDPR. As businesses evaluate their security posture in 2026, understanding how cloud based security services operate, what they protect, and how to implement them effectively has become a strategic imperative for IT leaders and decision-makers.
Understanding the Architecture of Cloud Based Security Services
Cloud based security services represent a fundamental shift from perimeter-based defences to distributed, identity-centric protection models. These services operate across multiple layers of the technology stack, delivering security controls that scale dynamically with business needs. Moreover, they integrate seamlessly with existing infrastructure whilst providing centralised visibility and policy enforcement across hybrid and multi-cloud environments.
The Shared Responsibility Model
One of the most critical concepts in cloud security is understanding the shared responsibility model between cloud providers and customers. This framework delineates which security controls each party manages, preventing dangerous gaps in protection. Therefore, organisations must clearly comprehend their obligations when implementing cloud based security services.
The division of responsibility varies by service model:
| Service Model | Provider Secures | Customer Secures |
|---|---|---|
| IaaS | Physical infrastructure, hypervisor, network | Operating systems, applications, data, identity, endpoints |
| PaaS | Infrastructure, OS, runtime environment | Applications, data, access controls, authentication |
| SaaS | Infrastructure, platform, application security | User access, data classification, configuration |
Understanding this division is essential because AWS notes in their shared responsibility overview that customers remain responsible for securing data, managing identities, and protecting endpoints regardless of service model. Consequently, cloud based security services must address both the customer-controlled elements and the integration points with provider-managed infrastructure.
Zero Trust Architecture in Cloud Environments
Modern cloud based security services increasingly incorporate Zero Trust principles, which assume no user, device, or network should be automatically trusted. This approach requires continuous verification of every access request based on multiple contextual factors. Furthermore, it eliminates the concept of a trusted internal network, recognising that threats can originate from anywhere.
Key components of Zero Trust in cloud security include:
- Identity verification through multi-factor authentication and behavioural analysis
- Device posture assessment before granting access to resources
- Least-privilege access with just-in-time permissions
- Micro-segmentation to limit lateral movement
- Continuous monitoring and automated threat response
Nevertheless, implementing Zero Trust requires careful orchestration of multiple security services and a clear understanding of data flows throughout your environment.
Core Components of Comprehensive Cloud Based Security Services
Effective cloud security requires multiple specialised services working in concert to address different threat vectors and compliance requirements. Each component plays a distinct role in the overall security architecture.
Identity and Access Management
Identity has become the new security perimeter in cloud environments. Therefore, robust identity and access management (IAM) controls form the foundation of cloud based security services. These systems govern who can access which resources under what conditions, whilst maintaining detailed audit trails for compliance purposes.
Modern IAM solutions provide:
- Centralised authentication across all cloud services and applications
- Role-based access control (RBAC) with granular permission sets
- Conditional access policies based on user location, device health, and risk level
- Privileged access management for administrative accounts
- Automated provisioning and de-provisioning tied to HR systems
Moreover, IAM services increasingly incorporate adaptive authentication that adjusts security requirements based on contextual risk, balancing security with user experience.
Data Protection and Encryption
Protecting data throughout its lifecycle remains paramount for businesses handling sensitive information. Cloud based security services deliver encryption both at rest and in transit, ensuring data remains unreadable to unauthorised parties. Additionally, advanced services provide tokenisation, data loss prevention (DLP), and rights management capabilities.
The Google Cloud guidance on customer-managed encryption keys demonstrates best practices for maintaining control over encryption keys whilst leveraging cloud infrastructure. This approach allows organisations to meet regulatory requirements whilst benefiting from cloud scalability.
| Protection Method | Use Case | Key Benefit |
|---|---|---|
| AES-256 Encryption | Data at rest in storage systems | Industry-standard confidentiality protection |
| TLS 1.3 | Data in transit between services | Protection against interception and tampering |
| Customer-Managed Keys | Regulated data requiring key control | Sovereignty and compliance adherence |
| Data Loss Prevention | Preventing unauthorised data exfiltration | Policy-based blocking of sensitive data transfers |
For European businesses concerned about data sovereignty, solutions such as vBoxxCloud provide GDPR-compliant storage with 256-bit AES encryption in ISO 27001-certified data centres located in the Netherlands, completely outside the reach of the US CLOUD Act.
Threat Detection and Response
Cloud based security services incorporate sophisticated threat detection capabilities that analyse vast quantities of telemetry data to identify anomalous behaviour and potential attacks. These services leverage machine learning and threat intelligence to detect threats that traditional signature-based approaches would miss. Furthermore, they provide automated response capabilities that can contain threats within seconds of detection.
Modern threat detection encompasses:
- Security information and event management (SIEM) for centralised log analysis
- User and entity behaviour analytics (UEBA) for anomaly detection
- Endpoint detection and response (EDR) across devices
- Cloud workload protection platforms for server and container security
- Extended detection and response (XDR) for correlated threat analysis
Advanced Security Service Delivery Models
As cloud security requirements have evolved, new delivery models have emerged that provide comprehensive protection whilst simplifying deployment and management. These approaches consolidate multiple security functions into unified platforms.
Security Service Edge and SASE Frameworks
The convergence of networking and security has produced two related architectures: Security Service Edge (SSE) and Secure Access Service Edge (SASE). TechTarget's comparison of SASE and SSE explains how these cloud-delivered models combine security functions with network connectivity. Therefore, organisations can enforce consistent policies regardless of where users and workloads are located.
SSE components typically include:
- Secure web gateway (SWG) for URL filtering and malware scanning
- Cloud access security broker (CASB) for SaaS application protection
- Zero Trust network access (ZTNA) for application access
- Data loss prevention integrated across all traffic flows
Nevertheless, implementing these frameworks requires careful planning to ensure performance remains acceptable whilst security improves.
Cloud Security Posture Management
Misconfiguration remains one of the leading causes of cloud security breaches. Cloud Security Posture Management (CSPM) services continuously assess cloud infrastructure against security best practices and compliance frameworks. Moreover, Deloitte's research on CSPM demonstrates how these tools reduce risk by identifying vulnerabilities before attackers can exploit them.
CSPM capabilities include:
- Automated compliance assessment against CIS benchmarks, GDPR, and industry frameworks
- Misconfiguration detection for storage buckets, network rules, and access policies
- Drift detection identifying unauthorised infrastructure changes
- Remediation workflows with automated or guided fixes
- Risk scoring to prioritise remediation efforts
Furthermore, CSPM integrates with infrastructure-as-code pipelines to prevent misconfigurations from reaching production environments.
Compliance and Regulatory Considerations for European Businesses
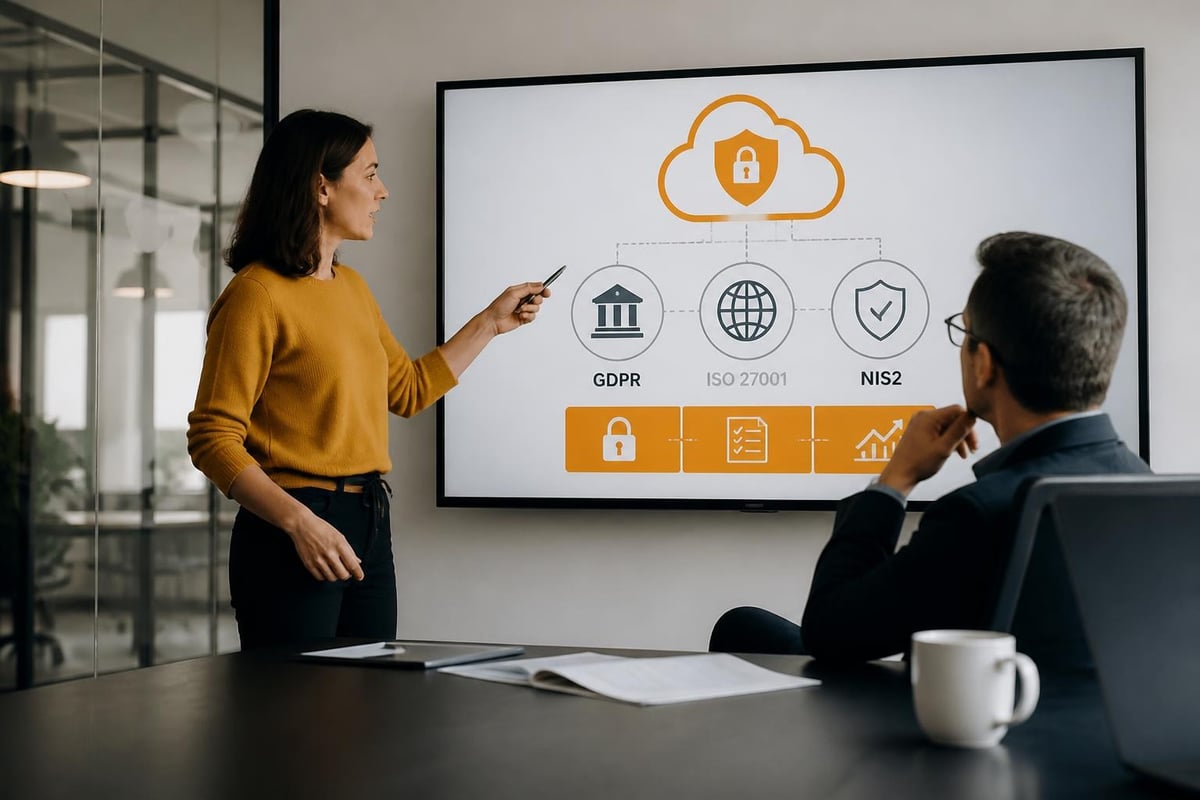
European organisations face unique compliance requirements that influence their selection and implementation of cloud based security services. GDPR mandates strict controls over personal data processing, storage, and transfer. Additionally, sector-specific regulations such as NIS2 for critical infrastructure and DORA for financial services impose further obligations.
Data Residency and Sovereignty
Data residency requirements necessitate that certain types of information remain within specific geographic boundaries. Therefore, businesses must verify that their cloud based security services store and process data in compliant locations. Many organisations prioritise European cloud storage to ensure data never leaves the continent.
Key considerations include:
- Physical server location within EU/EEA territories
- Data routing ensuring traffic doesn't transit through non-compliant jurisdictions
- Provider jurisdiction to avoid extraterritorial legal obligations
- Subprocessor locations for any third-party service dependencies
Moreover, businesses should review providers' data centre certifications to verify appropriate security controls and audit compliance.
Audit Trails and Forensic Readiness
Regulatory frameworks increasingly require organisations to maintain comprehensive audit trails of all access and modifications to sensitive data. Cloud based security services must provide detailed logging with tamper-proof storage. Furthermore, NIST's cloud forensics guidance establishes best practices for maintaining forensic readiness in cloud environments, ensuring organisations can investigate incidents effectively.
Essential audit capabilities include:
| Requirement | Security Service Feature | Compliance Benefit |
|---|---|---|
| Immutable logs | Write-once storage for audit records | Prevents tampering with evidence |
| Detailed access logs | Authentication and authorisation records | Demonstrates compliance with least privilege |
| Data lineage tracking | Complete history of data modifications | Supports GDPR accountability requirements |
| Retention management | Automated lifecycle policies | Balances compliance with storage costs |
Implementation Strategies for Cloud Based Security Services
Successfully deploying cloud based security services requires a structured approach that balances security effectiveness with operational practicality. Furthermore, organisations must consider their existing infrastructure, skill sets, and business requirements when planning implementation.
Assessment and Planning Phase
Before selecting specific services, conduct a thorough assessment of your current security posture and cloud environment. This evaluation should identify:
- Critical assets and data requiring protection
- Compliance obligations applicable to your industry and geography
- Existing security gaps in current controls
- Integration requirements with legacy systems
- Skill gaps within your security team
Moreover, engage stakeholders from IT, legal, compliance, and business units to ensure requirements are comprehensive. The Cloud Security Alliance's Cloud Controls Matrix provides a vendor-neutral framework for assessing security capabilities and mapping them to regulatory requirements.
Phased Deployment Approach
Rather than attempting a wholesale migration to cloud based security services, organisations typically benefit from a phased approach that builds capability incrementally:
- Establish foundational controls including IAM, encryption, and logging
- Deploy threat detection across initial cloud workloads
- Extend protection to additional environments and use cases
- Integrate advanced capabilities such as CSPM and automated response
- Optimise and mature policies based on operational experience
Nevertheless, each phase should deliver measurable security improvements whilst minimising disruption to business operations.
Training and Skill Development
Cloud based security services introduce new technologies and operational models that may differ significantly from traditional approaches. Therefore, investing in team training ensures effective utilisation of security capabilities. Consider both vendor-specific certifications and broader cloud security frameworks such as CCSP (Certified Cloud Security Professional).
Additionally, organisations should document runbooks and response procedures tailored to their specific cloud security architecture, ensuring consistent incident handling regardless of which team member responds.
Integration with Existing Infrastructure
Most businesses operate hybrid environments combining on-premises systems, private cloud, and public cloud services. Therefore, cloud based security services must integrate seamlessly across this heterogeneous landscape whilst providing unified visibility and control.
Hybrid Security Architecture
Effective hybrid security requires careful orchestration of controls across different environments. Furthermore, security policies must remain consistent regardless of where workloads execute. This consistency prevents attackers from exploiting weaker controls in legacy systems to gain access to cloud resources.
Key integration points include:
- Single sign-on extending on-premises identity to cloud services
- Unified threat intelligence sharing indicators across all environments
- Consistent policy enforcement using cloud-delivered security controls
- Centralised monitoring aggregating logs from all sources
- Coordinated incident response across hybrid infrastructure
Moreover, organisations should evaluate how cloud based security services interact with existing security controls to identify potential conflicts or gaps in coverage.
API Security and Service Integration
As businesses increasingly connect cloud services through APIs, securing these integration points becomes critical. Cloud based security services must provide API gateways, authentication mechanisms, and monitoring capabilities specifically designed for API traffic. Furthermore, API security should extend beyond simple authentication to include rate limiting, input validation, and abuse detection.
Consider implementing:
- API discovery to identify all exposed endpoints
- OAuth 2.0 and OpenID Connect for standardised authentication
- API gateway for centralised policy enforcement
- Behavioural analysis detecting anomalous API usage patterns
- Automated testing for API vulnerabilities
Evaluating Cloud Based Security Service Providers
Selecting appropriate providers for cloud based security services requires careful evaluation of technical capabilities, compliance credentials, and operational reliability. European businesses should prioritise providers who understand regional requirements and maintain infrastructure within appropriate jurisdictions.
Critical Evaluation Criteria
When assessing potential providers, examine these factors:
| Criterion | What to Evaluate | Why It Matters |
|---|---|---|
| Data location | Physical infrastructure geography | GDPR compliance and data sovereignty |
| Certifications | ISO 27001, SOC 2, industry-specific standards | Demonstrates security maturity and audit compliance |
| Incident response | Response times, escalation procedures, transparency | Minimises impact of security events |
| Integration capabilities | APIs, pre-built connectors, documentation | Reduces implementation complexity |
| Scalability | Performance under load, growth accommodation | Ensures service remains effective as usage increases |
Additionally, verify the provider's own security practices, including how they protect customer data, manage vulnerabilities, and respond to incidents affecting their infrastructure.
European vs. Global Providers
European businesses often face a choice between global hyperscale cloud providers and regional specialists. Whilst global providers offer extensive services and geographic reach, European providers may offer advantages in data protection compliance and regulatory alignment. Furthermore, European providers typically operate outside the jurisdiction of extraterritorial laws such as the US CLOUD Act, providing additional protection for sensitive data.
Consider these trade-offs when making provider selections, ensuring your choice aligns with your risk tolerance, compliance requirements, and operational needs.
Monitoring and Continuous Improvement
Implementing cloud based security services represents the beginning, not the end, of your security journey. Threats evolve constantly, and security controls require ongoing refinement to remain effective. Therefore, establish continuous monitoring processes and regular review cycles.
Security Metrics and KPIs
Effective security management requires measurable indicators of performance and risk. Define metrics that provide actionable insights rather than vanity numbers. Key performance indicators might include:
- Mean time to detect (MTTD) for security incidents
- Mean time to respond (MTTR) once threats are identified
- Policy violation rates indicating control effectiveness
- Coverage percentage of assets protected by security services
- Compliance audit findings tracking remediation progress
Moreover, trend these metrics over time to identify improvements or emerging issues requiring attention.
Regular Security Reviews
Schedule periodic reviews of your cloud based security services configuration and effectiveness. These reviews should assess:
- Policy alignment with current business requirements and threat landscape
- Access rights removing unnecessary permissions and inactive accounts
- Service coverage ensuring new workloads receive appropriate protection
- Incident patterns identifying recurring issues requiring architectural changes
- Compliance status against evolving regulatory requirements
Furthermore, conduct annual penetration testing and vulnerability assessments specifically targeting your cloud infrastructure to validate that security controls function as intended.
Cost Management for Cloud Based Security Services
Security services represent a significant investment, and costs can escalate quickly without proper management. Nevertheless, the expense of implementing comprehensive cloud based security services typically proves far lower than the potential cost of a major data breach. Therefore, organisations should view security expenditure as risk mitigation rather than overhead.
Optimising Security Spend
To maximise value from security investments:
- Consolidate vendors where possible to reduce complexity and negotiate better pricing
- Right-size services matching capacity to actual requirements rather than peak theoretical needs
- Leverage automation to reduce manual operational costs
- Monitor usage patterns identifying unused or underutilised services
- Consider reserved capacity for predictable baseline requirements
Additionally, factor in the total cost of ownership including training, integration effort, and ongoing management when comparing solutions.
Demonstrating Security ROI
Quantifying the return on investment for cloud based security services challenges many organisations. Nevertheless, consider these approaches:
- Calculate risk reduction based on likelihood and impact of prevented incidents
- Measure efficiency gains from automation replacing manual security tasks
- Track compliance cost avoidance through built-in controls reducing audit expenses
- Document incident cost savings comparing breach scenarios with and without controls
- Assess business enablement where security services allow new initiatives
Cloud based security services provide the comprehensive, scalable protection that modern European businesses require to operate safely in increasingly distributed environments. By understanding the shared responsibility model, implementing layered controls, and maintaining continuous improvement practices, organisations can achieve robust security whilst meeting stringent compliance obligations. vBoxx delivers European-hosted security solutions including encrypted cloud storage, secure communications, and password management, all running on ISO 27001-certified infrastructure in the Netherlands with full GDPR compliance and protection from extraterritorial data access laws. Explore how vBoxx's comprehensive suite can strengthen your security posture whilst supporting your digital transformation initiatives.