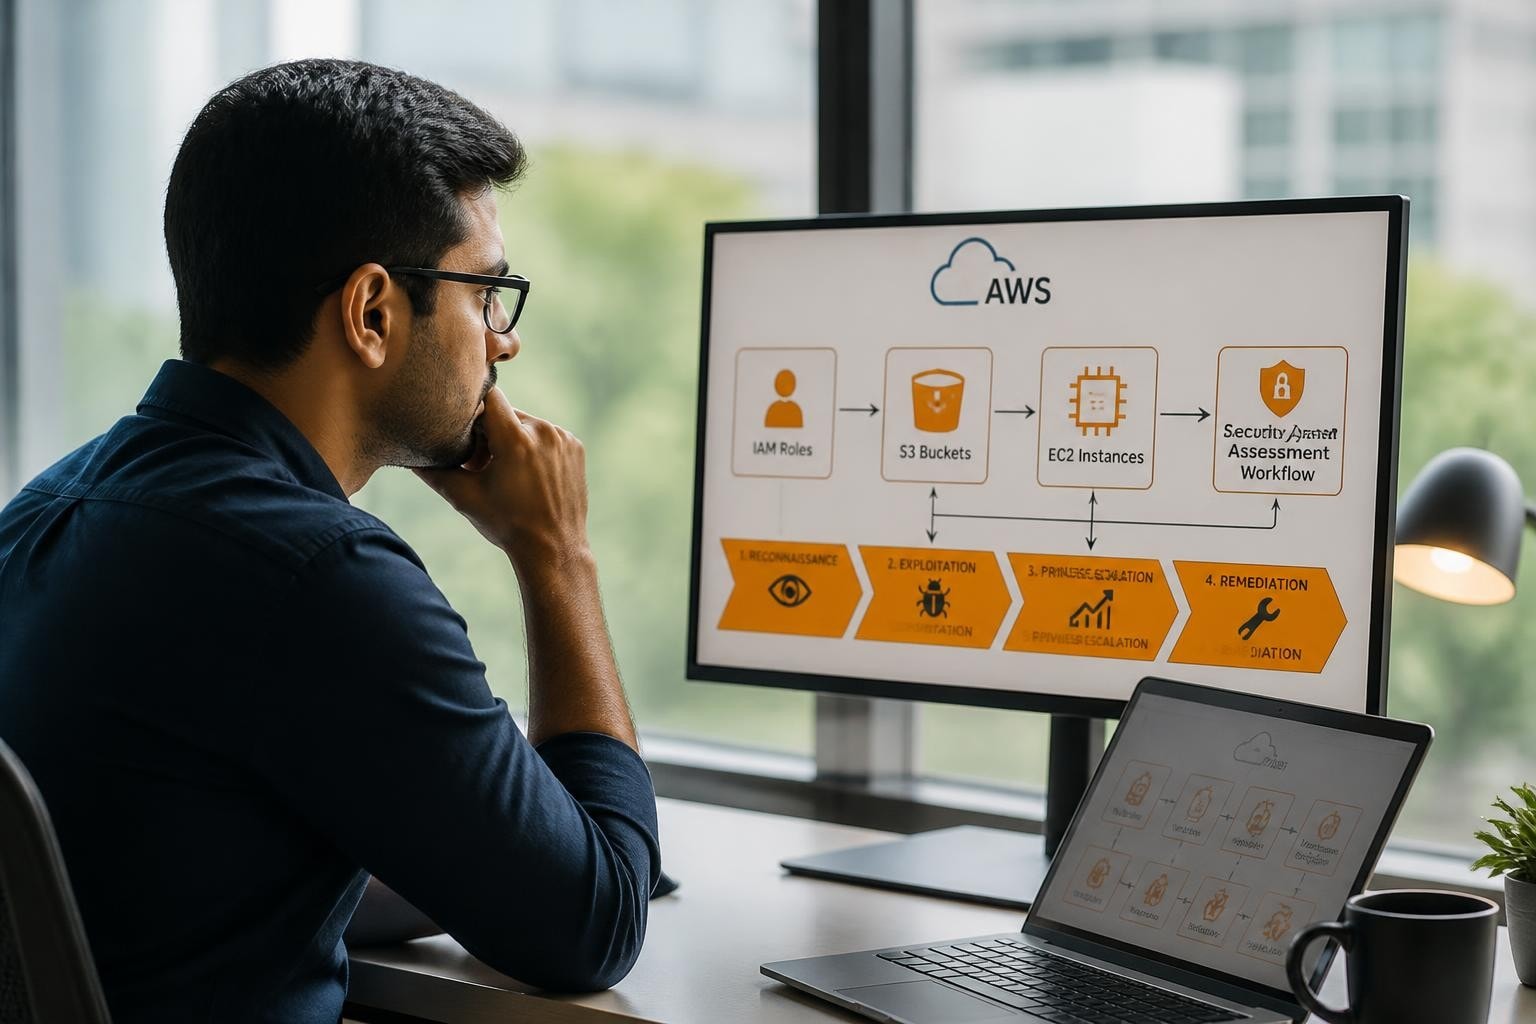
As organisations increasingly migrate critical workloads to Amazon Web Services, the attack surface expands beyond traditional on-premises infrastructure. Consequently, security teams must adopt sophisticated testing methodologies to identify vulnerabilities before malicious actors exploit them. AWS pentesting has evolved into a specialised discipline that requires both cloud-native expertise and traditional offensive security skills. Moreover, European businesses face unique compliance challenges that make thorough security assessments even more critical.
Understanding the AWS Pentesting Landscape
AWS pentesting differs fundamentally from traditional network penetration testing. Furthermore, the shared responsibility model means that whilst AWS secures the underlying infrastructure, customers remain accountable for securing their applications, data, and configurations. Therefore, penetration testers must understand where their responsibilities begin and which services fall within scope.
The cloud environment introduces unique attack vectors that simply do not exist in conventional data centres. Nevertheless, many organisations approach AWS security assessments with outdated methodologies. In addition, the dynamic nature of cloud resources means that today's secure configuration can become tomorrow's vulnerability through a single API call or infrastructure-as-code deployment.
Regulatory Frameworks and Compliance
European businesses operating AWS workloads must navigate multiple regulatory frameworks simultaneously. The GDPR mandates robust security measures and regular assessments, whilst sector-specific regulations add additional layers of complexity. Moreover, organisations storing data in AWS must ensure their testing activities comply with data protection requirements.
Industry standards provide essential guidance for structuring security assessments. The NIST SP 800-115 publication offers comprehensive methodologies for planning and executing technical security assessments. Furthermore, Cloud Security Alliance research delivers cloud-specific testing frameworks that address modern threats.
| Regulatory Framework | Key Requirements | Impact on Testing |
|---|---|---|
| GDPR | Data protection by design, breach notification | Requires testing of encryption, access controls, audit logging |
| ISO 27001 | Information security management system | Mandates regular security assessments and risk evaluation |
| NIS2 Directive | Critical infrastructure protection | Demands comprehensive pentesting for essential services |
| eIDAS | Electronic identification and trust services | Requires secure authentication and signature verification testing |
AWS Pentesting Methodology and Scope
A structured approach to AWS pentesting ensures comprehensive coverage whilst minimising operational disruption. Initially, security teams must define clear objectives, scope boundaries, and rules of engagement. Subsequently, they can execute testing phases that systematically examine each layer of the cloud environment.
Pre-Engagement and Planning
The planning phase determines the success of the entire engagement. Therefore, organisations must clearly document which AWS accounts, regions, and services fall within scope. In addition, teams should review the AWS penetration testing policy to understand permitted activities and notification requirements.
Rules of engagement should address several critical considerations:
- Timing windows: Specify when testing can occur to avoid business-critical periods
- Throttling limits: Define maximum request rates to prevent service disruption
- Data handling: Establish protocols for managing sensitive information discovered during testing
- Escalation procedures: Document communication channels for critical findings
- Restoration plans: Prepare rollback procedures for configuration changes
Furthermore, penetration testers should establish baseline configurations before testing begins. This documentation proves invaluable when distinguishing test artefacts from genuine security incidents. Moreover, it enables accurate post-engagement cleanup and verification.
Reconnaissance and Information Gathering
The reconnaissance phase maps the target environment's attack surface. Initially, testers enumerate public-facing resources, DNS records, and exposed services. Subsequently, they identify potential entry points and prioritise targets based on risk and business impact.
External reconnaissance techniques include:
- DNS enumeration: Discover subdomains, S3 bucket names, and CloudFront distributions
- Certificate transparency logs: Identify additional domains and services
- Public code repositories: Search for accidentally committed credentials or configuration files
- Metadata services: Attempt to access instance metadata from external positions
- API gateway discovery: Enumerate publicly accessible API endpoints
Nevertheless, internal reconnaissance often yields more valuable intelligence. Once initial access is obtained, testers can enumerate IAM permissions, discover additional resources, and map trust relationships between accounts. Therefore, tools like Pacu become essential for systematically exploring the AWS environment and identifying privilege escalation paths.
Exploitation and Privilege Escalation
After reconnaissance, penetration testers attempt to exploit identified vulnerabilities. Furthermore, they chain multiple weaknesses together to demonstrate realistic attack scenarios. The MITRE ATT&CK framework provides a structured taxonomy for mapping techniques and tactics observed during cloud assessments.
Common AWS Vulnerabilities
AWS environments frequently exhibit several categories of security weaknesses. Firstly, overly permissive IAM policies grant excessive privileges that enable lateral movement. Secondly, misconfigured S3 buckets expose sensitive data to unauthorised parties. Additionally, inadequate network segmentation allows attackers to pivot between resources.
Identity and Access Management Flaws
IAM misconfigurations represent the most common vulnerability class in AWS pentesting. Moreover, privilege escalation through IAM often provides the fastest path to complete environment compromise. Attackers exploit several patterns repeatedly:
- Policies granting
iam:AttachUserPolicyoriam:PutUserPolicypermissions - Lambda execution roles with excessive privileges
- Cross-account role trust relationships lacking external ID validation
- Unused credentials and access keys in legacy applications
- Service-linked roles with overly broad permissions
Storage and Data Exposure
S3 bucket misconfigurations continue to cause major data breaches. Nevertheless, organisations repeatedly deploy buckets with public read permissions or overly permissive bucket policies. In addition, testers frequently discover encryption disabled on sensitive data stores.
| Vulnerability Type | Common Causes | Exploitation Impact |
|---|---|---|
| Public S3 buckets | Default-allow policies, ACL misconfigurations | Data exfiltration, compliance violations |
| Unencrypted volumes | Missing encryption requirements in templates | Compliance failures, data exposure |
| Snapshot exposure | Public snapshot permissions, cross-account sharing | Volume mounting, data access |
| Database credentials | Hardcoded in code, stored in S3 | Complete database compromise |
Advanced Attack Techniques
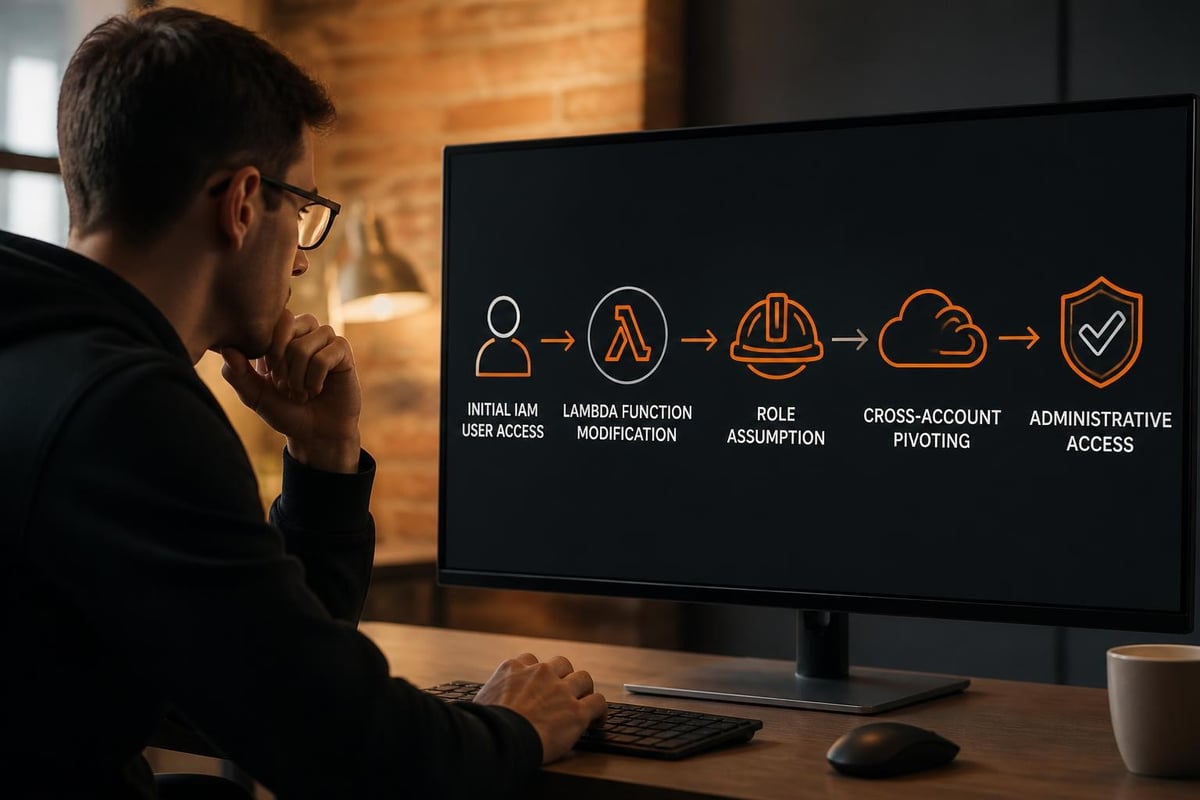
Sophisticated adversaries employ techniques beyond simple misconfigurations. Furthermore, they exploit the interconnected nature of cloud services to move laterally. NetSPI's research on AWS Organizations demonstrates how attackers pivot across account boundaries to compromise entire cloud estates.
Consequently, penetration testers must examine these advanced scenarios:
- Lambda function poisoning: Modify event-driven functions to exfiltrate data or establish persistence
- Systems Manager exploitation: Leverage SSM access to execute commands on EC2 fleets
- Secrets Manager enumeration: Extract credentials from centralised secret stores
- CloudFormation manipulation: Inject malicious resources through template updates
- Container escape: Break out of ECS or EKS containers to access underlying hosts
Testing Cloud-Native Applications
Modern AWS deployments increasingly rely on serverless architectures and containerised workloads. Therefore, AWS pentesting must extend beyond infrastructure to examine application-layer security. The OWASP Cloud-Native Application Security Top 10 identifies risks specific to these deployment patterns.
API Gateway and Serverless Security
API Gateway services frequently expose backend systems to the internet. Moreover, inadequate authentication and authorisation controls enable unauthorised access. Testers should examine several attack surfaces:
- Missing authentication: APIs lacking proper identity verification
- Broken object-level authorisation: Insufficient access control between resources
- Mass assignment: APIs accepting unintended parameters that modify protected fields
- Rate limiting absence: Endpoints vulnerable to abuse and denial of service
- Injection vulnerabilities: SQL, NoSQL, and command injection in Lambda functions
Furthermore, serverless functions introduce unique security considerations. Lambda functions often run with excessive IAM permissions, creating privilege escalation opportunities. Additionally, environment variables frequently contain sensitive credentials accessible to anyone who can read function configurations.
Container and Orchestration Security
ECS and EKS deployments require specialised testing approaches. Initially, testers examine container images for known vulnerabilities and misconfigurations. Subsequently, they assess the orchestration layer for privilege escalation paths and lateral movement opportunities.
Container-specific test cases include:
- Image vulnerability scanning: Identify outdated packages and known CVEs
- Secrets management: Verify secure credential injection rather than environment variables
- Network policies: Test pod-to-pod communication restrictions
- RBAC configurations: Attempt privilege escalation through Kubernetes service accounts
- Host access: Evaluate container escape possibilities and node compromise scenarios
Nevertheless, many organisations overlook the importance of secure baseline configurations. Therefore, European cloud infrastructure providers that implement security by design can reduce the attack surface before applications even deploy.
Remediation and Continuous Security
AWS pentesting generates actionable findings, but remediation determines actual security improvement. Furthermore, cloud environments change continuously, necessitating ongoing assessment rather than annual point-in-time tests. Consequently, organisations should integrate security testing throughout the development lifecycle.
Prioritising and Addressing Findings
Effective remediation begins with proper risk prioritisation. Moreover, findings should map to business impact rather than relying solely on technical severity scores. In addition, remediation recommendations must account for operational constraints and architectural dependencies.
Immediate Actions
Critical findings require emergency response procedures:
- Credential rotation: Replace exposed access keys and passwords immediately
- Permission revocation: Remove excessive IAM privileges pending proper scoping
- Resource isolation: Network-isolate compromised instances for forensic analysis
- Public access removal: Close unintended public exposure on storage and databases
- Patch deployment: Apply security updates to vulnerable services and applications
Strategic Improvements
Long-term security enhancement requires architectural changes. Therefore, organisations should implement defence-in-depth strategies that combine multiple security controls. Furthermore, infrastructure-as-code enables consistent security baselines across all deployments.
| Security Control Layer | Implementation Approach | Measurement Metric |
|---|---|---|
| Identity | Least privilege IAM policies, MFA enforcement | Percentage of policies using wildcards |
| Network | Security groups, NACLs, VPC isolation | Exposed ports and services count |
| Data | Encryption at rest and in transit, key rotation | Unencrypted resource percentage |
| Logging | CloudTrail, VPC Flow Logs, GuardDuty | Log coverage across accounts |
| Detection | Automated alerts, anomaly detection | Mean time to detection |
Building a Continuous Security Programme
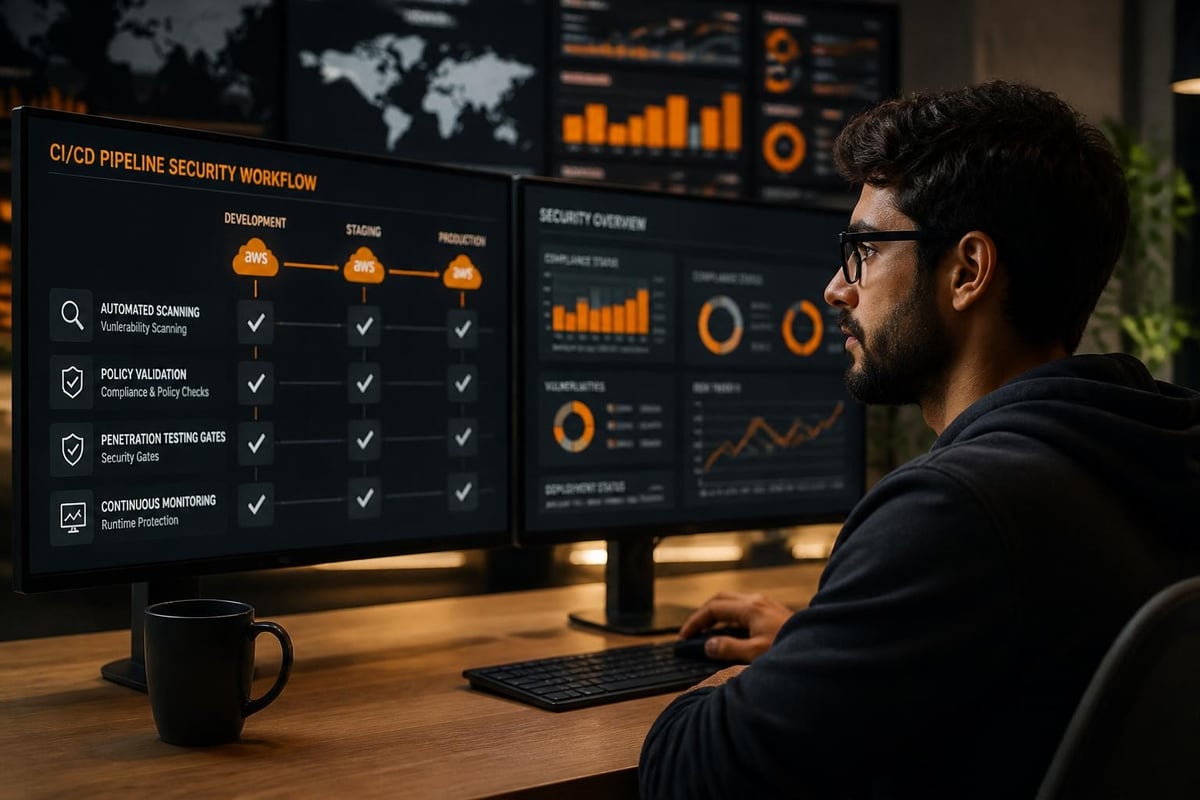
Annual penetration tests provide snapshots, but continuous security requires ongoing assessment. Moreover, integrating security testing into deployment pipelines catches vulnerabilities before production release. SANS cloud penetration testing resources offer practical guidance for implementing continuous security validation.
Continuous security programmes incorporate multiple assessment types:
- Automated vulnerability scanning: Daily scans of infrastructure and applications
- Policy compliance checks: Continuous validation against security baselines
- Threat modelling: Regular review of architecture changes and new services
- Purple team exercises: Collaborative detection and response testing
- Bug bounty programmes: Crowdsourced security research on production systems
Furthermore, organisations should establish clear metrics for measuring security programme effectiveness. Therefore, tracking remediation velocity, vulnerability recurrence, and security debt provides actionable insights for continuous improvement.
Vendor Management and Third-Party Risk
Many organisations rely on AWS through managed service providers or use third-party applications deployed on AWS infrastructure. Consequently, AWS pentesting must extend to vendors and suppliers with access to your cloud environment. Moreover, European businesses must ensure vendors comply with GDPR and data sovereignty requirements.
Assessing Cloud Service Providers
When evaluating European cloud providers, security assessments should verify several critical aspects. Initially, confirm that infrastructure resides in European data centres and falls outside extraterritorial data access laws. Subsequently, review the provider's own security certifications and penetration testing programme.
For instance, organisations using secure hosting infrastructure should verify ISO 27001 certification, encryption standards, and physical security controls. In addition, providers should demonstrate regular third-party security assessments and transparent vulnerability disclosure processes.
Key Vendor Security Questions
- Where is data physically stored, and which jurisdictions have legal access?
- How frequently do you conduct penetration testing and security audits?
- What is your process for handling vulnerability reports?
- How do you segregate customer environments and prevent cross-tenant access?
- What security controls protect administrative access to customer resources?
Supply Chain Security
Third-party libraries, container images, and Lambda layers introduce supply chain risks. Nevertheless, many organisations fail to inventory dependencies or monitor for vulnerabilities. Therefore, AWS pentesting should include supply chain analysis and software composition assessment.
Effective supply chain security requires:
- Dependency tracking: Maintain inventories of all third-party components
- Vulnerability monitoring: Subscribe to security advisories for used packages
- Image signing: Verify container image authenticity and integrity
- Code review: Examine third-party code for backdoors and malicious functionality
- Least privilege: Restrict third-party component permissions to minimum requirements
Building Internal Security Capabilities
Whilst external penetration testing provides valuable independent assessment, organisations should develop internal security capabilities. Furthermore, training development teams in secure cloud practices prevents vulnerabilities more effectively than discovering them post-deployment. Moreover, internal red teams can conduct continuous testing throughout the year.
Security Training and Awareness
Developers, architects, and operations teams require cloud security knowledge appropriate to their roles. Therefore, organisations should invest in training programmes that cover AWS-specific threats and secure configuration practices. In addition, regular security awareness campaigns keep cloud security top-of-mind.
Effective training programmes address:
- Secure coding practices: Input validation, output encoding, and secure API design
- IAM best practices: Least privilege, role separation, and credential management
- Data protection: Encryption implementation, key management, and data classification
- Incident response: Detecting, containing, and recovering from security incidents
- Compliance requirements: GDPR, industry regulations, and contractual obligations
Furthermore, hands-on lab environments enable teams to practice security testing safely. Consequently, organisations can build muscle memory for secure defaults and defensive coding patterns.
Tool Selection and Automation
Successful AWS pentesting requires the right toolset. Moreover, automation enables comprehensive coverage that manual testing cannot achieve alone. Nevertheless, tools must be carefully selected and configured to avoid false positives and operational disruption.
Essential AWS Security Testing Tools
| Tool Category | Examples | Primary Use Case |
|---|---|---|
| IAM analysis | ScoutSuite, Prowler, CloudMapper | Permission enumeration and privilege escalation detection |
| Exploitation | Pacu, CloudGoat, AWS pwn | Offensive testing and attack path validation |
| Compliance | AWS Config, CloudCustodian, Dome9 | Policy validation and configuration baseline enforcement |
| Secrets detection | TruffleHog, GitLeaks, detect-secrets | Credential exposure in code repositories and configurations |
| Container security | Trivy, Clair, Anchore | Image vulnerability scanning and policy enforcement |
In addition, organisations should integrate security testing tools into CI/CD pipelines. Therefore, every code commit and infrastructure change undergoes automated security validation before deployment. Moreover, shift-left security practices catch vulnerabilities during development when remediation costs remain lowest.
AWS pentesting requires specialised expertise, structured methodologies, and continuous assessment to protect modern cloud environments effectively. Moreover, European organisations must balance comprehensive security testing with strict data protection compliance and sovereignty requirements. If you're seeking a cloud infrastructure partner that prioritises security, GDPR compliance, and European data sovereignty, vBoxx operates ISO 27001-certified data centres in the Netherlands with comprehensive security controls built into every service. Our infrastructure undergoes regular security assessments, and we provide the transparency and control that European businesses need to maintain robust cloud security whilst meeting regulatory obligations.