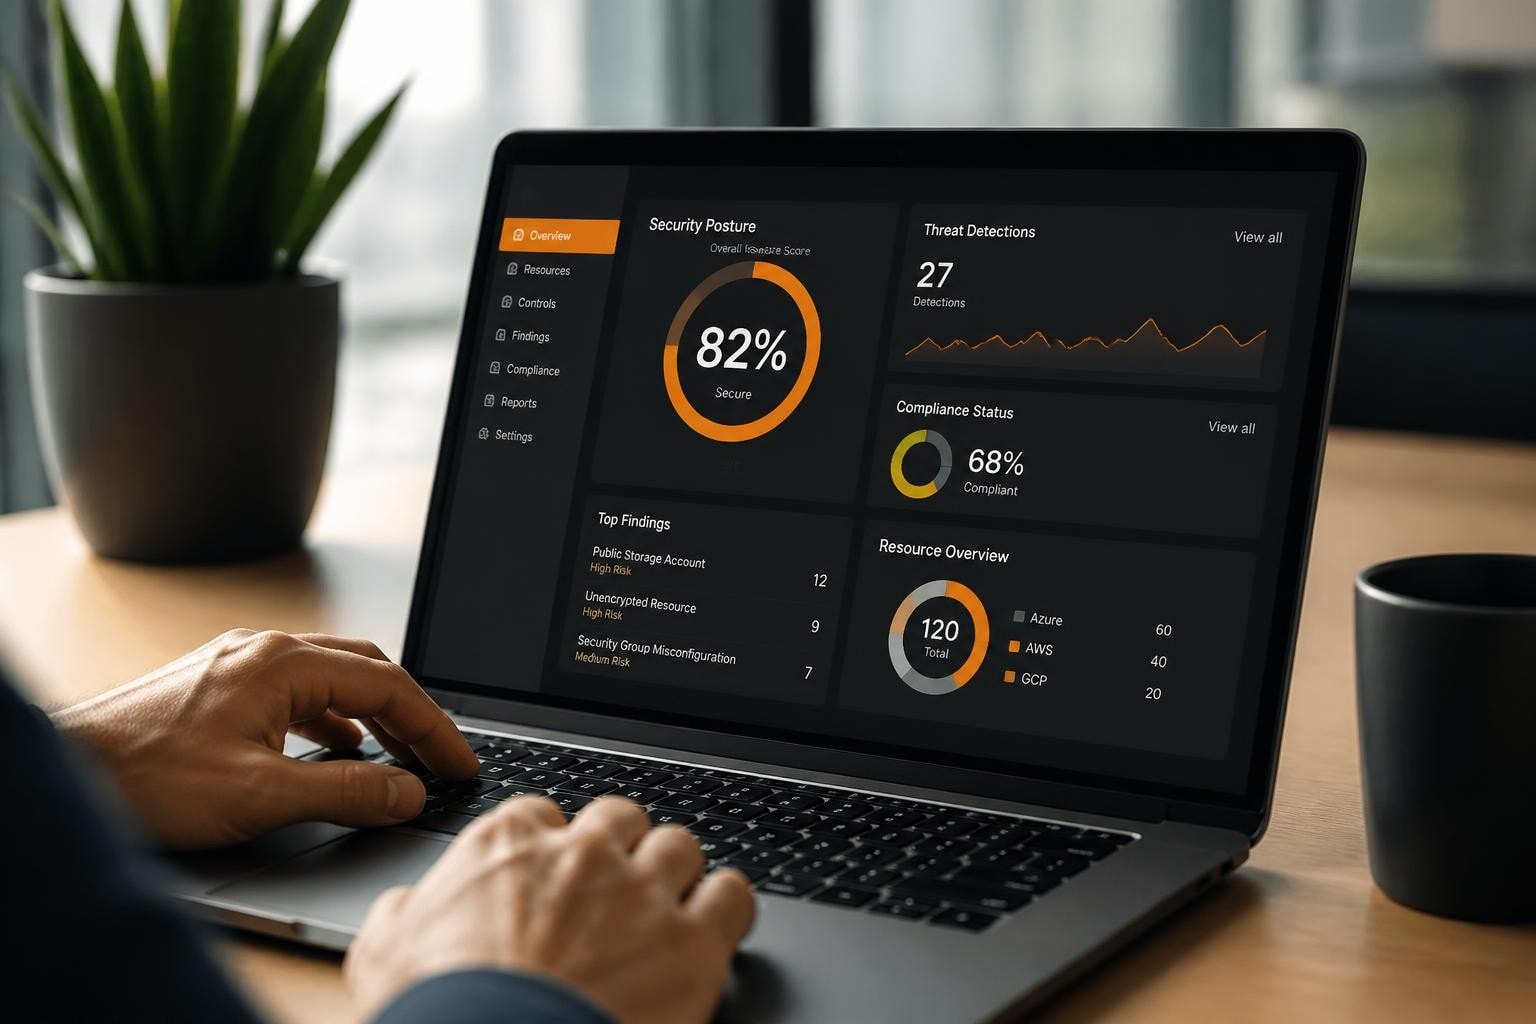
As businesses migrate critical workloads to cloud environments, the attack surface expands exponentially. Furthermore, traditional security tools often fall short when protecting dynamic, distributed infrastructure. Managed Detection and Response services specifically designed for Amazon Web Services have emerged as essential components of modern cybersecurity strategies, offering continuous monitoring, threat hunting, and automated incident response tailored to cloud-native architectures. This comprehensive approach to aws mdr combines advanced technology with human expertise to identify and neutralise threats before they cause significant damage.
Understanding AWS MDR Services
Managed Detection and Response for AWS represents a specialised security service that provides round-the-clock monitoring, threat detection, and incident response specifically optimised for Amazon Web Services environments. Unlike generic security solutions, aws mdr services integrate deeply with AWS-native tools and services, leveraging cloud infrastructure logs, configuration data, and behavioural analytics to identify potential threats.
These services typically combine several core components:
- Real-time monitoring of AWS CloudTrail, VPC Flow Logs, and GuardDuty alerts
- Automated threat detection using machine learning and behavioural analytics
- 24/7 security operations centre staffed by certified analysts
- Incident response capabilities with predefined playbooks
- Threat hunting to proactively identify hidden risks
- Compliance reporting aligned with regulatory requirements
Moreover, the integration between aws mdr providers and AWS services creates a seamless security layer that adapts to infrastructure changes automatically. Nevertheless, organisations must carefully evaluate providers based on their specific security requirements and compliance obligations.
Key Benefits of AWS MDR for Businesses
Implementing aws mdr services delivers substantial advantages beyond traditional security approaches. Firstly, businesses gain access to specialised expertise without building internal security operations teams, which can be prohibitively expensive and difficult to staff with qualified professionals. In addition, the automation capabilities significantly reduce response times from hours to minutes.
Enhanced Threat Detection Capabilities
Proficio’s Managed Detection and Response service for AWS demonstrates how real-time threat detection leverages multiple data sources simultaneously. Therefore, organisations benefit from correlation across CloudTrail logs, network traffic patterns, and application behaviours that would be impossible to analyse manually.
| Capability | Traditional Approach | AWS MDR Approach |
|---|---|---|
| Monitoring Coverage | Business hours only | 24/7/365 coverage |
| Detection Speed | Hours to days | Minutes to seconds |
| Response Time | Manual intervention required | Automated containment |
| Expertise Required | Multiple specialists needed | Included in service |
| Infrastructure Scaling | Linear cost increase | Elastic scaling included |
Furthermore, the integration of artificial intelligence enhances detection accuracy whilst reducing false positives. Daylight Security’s AI-Powered MDR service exemplifies this approach, combining human expertise with advanced AI algorithms to deliver superior protection and rapid response capabilities.
Cost Efficiency and Resource Optimisation
The financial advantages of aws mdr extend beyond simple cost comparison. Consequently, businesses avoid the substantial investment required for security infrastructure, specialist recruitment, training programmes, and ongoing technology updates. Additionally, the operational model shifts security spending from unpredictable capital expenditure to manageable operational costs.
Moreover, organisations reduce the indirect costs associated with security incidents. Research indicates that the average cost of a data breach continues to rise annually, with detection and containment representing significant portions of total expenses. Therefore, investing in proactive aws mdr services delivers measurable return on investment through incident prevention and rapid containment.
Compliance and Data Sovereignty Considerations
European businesses face unique challenges when implementing cloud security solutions, particularly regarding data protection regulations and jurisdictional concerns. Nevertheless, aws mdr services can be configured to meet stringent compliance requirements whilst maintaining operational efficiency.
The General Data Protection Regulation imposes strict obligations on organisations processing personal data of EU residents. Furthermore, businesses must consider where security telemetry and incident data are stored and processed. Consequently, selecting aws mdr providers that operate within European legal frameworks becomes crucial for maintaining compliance.
European Data Protection Requirements
Organisations subject to GDPR must ensure their security monitoring doesn't create additional compliance risks. In addition, the processing of security logs often involves personal data, requiring appropriate legal bases and safeguards. Therefore, aws mdr services must implement data minimisation, purpose limitation, and appropriate retention policies.
The recent European Commission’s scrutiny of major technology providers underscores the importance of selecting security solutions that prioritise data sovereignty. Similarly, businesses should evaluate whether their aws mdr provider stores security data in European data centres and operates under European jurisdiction.
For businesses requiring guaranteed European data residency, infrastructure providers like vBoxx offer ISO 27001-certified data centres in the Netherlands, ensuring GDPR compliance and protection from extraterritorial data access requests under frameworks such as the US CLOUD Act.
Implementing AWS MDR: Strategic Approach
Successful aws mdr implementation requires careful planning and phased execution. Moreover, organisations must align security objectives with business requirements, compliance obligations, and operational capabilities. The following structured approach ensures effective deployment whilst minimising disruption.
Phase 1: Assessment and Planning
- Inventory AWS resources across all regions and accounts
- Identify critical assets requiring prioritised protection
- Document compliance requirements and regulatory obligations
- Evaluate existing security controls and identify gaps
- Define success metrics and key performance indicators
Subsequently, organisations should develop a comprehensive implementation roadmap that addresses technical requirements, organisational changes, and stakeholder communication. Furthermore, establishing clear roles and responsibilities prevents confusion during incident response scenarios.
Phase 2: Provider Selection and Integration
Choosing the appropriate aws mdr provider demands thorough evaluation beyond pricing considerations. Secureworks’ Taegis MDR service and HCLTech’s Universal MDR platform represent different approaches to threat detection and response, each with distinct advantages for specific use cases.
Key evaluation criteria include:
- Detection capabilities across AWS services and third-party integrations
- Response automation and playbook customisation options
- Compliance certifications relevant to your industry
- Data residency and processing location
- Integration complexity with existing tools and workflows
- Escalation procedures and communication protocols
Additionally, organisations should request detailed service level agreements covering response times, availability guarantees, and performance commitments. Therefore, businesses can establish realistic expectations and accountability frameworks from the outset.
Advanced Threat Detection Techniques
Modern aws mdr services employ sophisticated techniques that extend beyond traditional signature-based detection. Nevertheless, understanding these methodologies helps organisations appreciate the value delivered by advanced security platforms and make informed decisions about service selection.
Behavioural Analytics and Machine Learning
Behavioural analytics establish baseline patterns for user activities, application behaviours, and network traffic within AWS environments. Consequently, deviations from established norms trigger alerts for investigation, even when attackers use novel techniques that evade signature-based detection. Furthermore, machine learning algorithms continuously refine these baselines, adapting to legitimate changes whilst maintaining sensitivity to genuine threats.
Research into multi-domain recommendation models provides insights into how complex systems can operate across various domains simultaneously, which parallels the challenges faced by aws mdr platforms monitoring diverse AWS services and application architectures.
Threat Intelligence Integration
Premium aws mdr services incorporate global threat intelligence feeds, enriching local detection capabilities with broader context about emerging attack patterns, known malicious actors, and vulnerability exploits. Moreover, this intelligence enables proactive defence measures before threats reach your environment.
The integration of threat intelligence delivers several operational benefits:
- Proactive blocking of known malicious IP addresses and domains
- Vulnerability prioritisation based on active exploitation in the wild
- Attack attribution linking incidents to known threat actor groups
- Predictive defence implementing controls against emerging techniques
In addition, next-generation MDR services leveraging AI demonstrate how artificial intelligence enhances threat intelligence application, automatically correlating disparate signals to identify sophisticated attack campaigns.
Incident Response and Containment Strategies
The true value of aws mdr becomes evident during security incidents when rapid, coordinated response minimises damage and recovery costs. Furthermore, well-designed incident response processes transform potential disasters into manageable events with minimal business impact.
Automated Response Playbooks
Modern aws mdr platforms implement automated response actions that execute immediately upon threat detection, significantly reducing attacker dwell time. Therefore, common threats like compromised credentials, unauthorised access attempts, and malware infections trigger predetermined containment measures without waiting for human intervention.
| Threat Type | Automated Response | Manual Escalation Trigger |
|---|---|---|
| Compromised IAM credentials | Disable credentials, revoke sessions | Persistent re-authentication attempts |
| Unauthorised security group changes | Revert to approved baseline | Changes from privileged accounts |
| Data exfiltration attempt | Block egress traffic, isolate instance | Large-scale systematic extraction |
| Malware detection | Quarantine instance, snapshot for forensics | Lateral movement detected |
Nevertheless, certain scenarios require human expertise and decision-making authority. Consequently, effective aws mdr services maintain clear escalation paths ensuring critical decisions receive appropriate oversight whilst routine responses proceed automatically.
Forensics and Root Cause Analysis
Following incident containment, thorough investigation determines attack vectors, assesses damage extent, and identifies necessary remediation steps. Moreover, real-world case studies demonstrate how comprehensive forensic analysis prevents recurrence and strengthens overall security posture.
Forensic investigations typically examine:
- Initial access vectors identifying how attackers breached defences
- Lateral movement patterns tracing attacker activities across infrastructure
- Data access and exfiltration determining information compromise scope
- Persistence mechanisms uncovering backdoors and ongoing access methods
- Timeline reconstruction establishing complete incident chronology
Optimising AWS MDR for Maximum Effectiveness
Deploying aws mdr services represents the foundation rather than the conclusion of a comprehensive security programme. Furthermore, continuous optimisation ensures your investment delivers maximum value whilst adapting to evolving threats and changing business requirements.
Integration with DevSecOps Practices
Modern application development methodologies demand security integration throughout the development lifecycle rather than as an afterthought. Consequently, aws mdr services should connect seamlessly with continuous integration and deployment pipelines, providing security feedback during development rather than discovering vulnerabilities in production.
Mission’s managed service for AWS threat detection exemplifies this integrated approach, embedding security monitoring directly into operational workflows. Therefore, development teams receive immediate visibility into security implications of infrastructure changes and application deployments.
Additionally, infrastructure-as-code practices enable security policies to be codified, version-controlled, and automatically enforced. Moreover, aws mdr platforms can monitor these configurations, alerting teams when deployments deviate from approved security baselines.
Continuous Tuning and Improvement
Initial aws mdr deployment typically generates numerous alerts requiring tuning to reduce false positives whilst maintaining detection sensitivity. Nevertheless, this tuning process demands ongoing attention rather than one-time configuration. Furthermore, as your AWS environment evolves, detection rules must adapt correspondingly.
Effective tuning strategies include:
- Regular alert review identifying patterns in false positives
- Baseline refinement updating normal behaviour definitions
- Rule customisation adapting generic detections to specific environment
- Feedback loops incorporating analyst insights into detection logic
- Metrics tracking monitoring detection accuracy and response efficiency
In addition, comparative analysis of MDR solutions helps organisations benchmark their security posture against industry standards and identify opportunities for enhancement.
Multi-Cloud and Hybrid Environment Considerations
Whilst this discussion focuses on aws mdr, many organisations operate multi-cloud or hybrid infrastructures combining AWS with on-premises systems or other cloud providers. Therefore, security strategies must address the complexity of distributed environments whilst maintaining consistent protection levels.
Unified Security Visibility
Managing security across disparate platforms creates challenges for centralised monitoring and coordinated response. Nevertheless, advanced aws mdr providers offer capabilities extending beyond pure AWS environments, providing unified dashboards and correlation across multiple infrastructure types.
Smarttech247’s MDR service for AWS demonstrates how modern platforms transform complex environments into well-monitored ecosystems with consistent security policies. Moreover, this unified approach simplifies compliance reporting and reduces operational overhead associated with managing multiple security tools.
Cross-Platform Threat Correlation
Sophisticated attacks often leverage multiple platforms simultaneously, exploiting the complexity of hybrid environments and inconsistent security controls between systems. Consequently, effective aws mdr implementation must correlate events across infrastructure boundaries, identifying attack patterns that span cloud and on-premises resources.
Furthermore, integration with identity providers, network security tools, and endpoint protection platforms creates comprehensive visibility that single-platform monitoring cannot achieve. Therefore, businesses should evaluate aws mdr providers based on their multi-platform capabilities even when AWS represents their primary infrastructure.
Measuring AWS MDR Success and ROI
Quantifying security investment returns presents inherent challenges since successful prevention leaves no visible evidence. Nevertheless, organisations can establish meaningful metrics demonstrating aws mdr value and guiding continuous improvement efforts.
Key Performance Indicators
Effective aws mdr measurement combines technical metrics with business-oriented indicators:
- Mean time to detect (MTTD) measuring how quickly threats are identified
- Mean time to respond (MTTR) tracking incident containment speed
- False positive rate indicating detection accuracy and analyst efficiency
- Coverage percentage showing monitored infrastructure proportion
- Compliance audit results demonstrating regulatory adherence
- Incident prevention rate estimating threats blocked proactively
Additionally, comparing these metrics against industry benchmarks provides context for performance evaluation. Moreover, tracking trends over time reveals whether security posture improves consistently or requires intervention.
Business Impact Assessment
Beyond technical metrics, aws mdr delivers measurable business benefits including reduced insurance premiums, enhanced customer trust, and competitive advantages in security-conscious markets. Furthermore, avoiding breach-related costs like regulatory fines, legal expenses, and reputation damage represents substantial but difficult-to-quantify value.
Organisations should document prevented incidents, near-miss scenarios, and security improvements attributable to aws mdr implementation. Therefore, annual reviews can demonstrate cumulative value and justify continued investment in comprehensive security programmes.
Future Trends in AWS MDR
The aws mdr landscape continues evolving rapidly as threats become more sophisticated and cloud environments grow increasingly complex. Nevertheless, several emerging trends promise to reshape how organisations approach cloud security in coming years.
Artificial intelligence integration will deepen significantly, moving beyond simple pattern matching to genuine predictive capabilities that anticipate attacks before they occur. Furthermore, quantum computing advances will eventually require fundamental changes to cryptographic practices, with aws mdr services adapting to protect against quantum-enabled threats.
Zero-trust architecture principles increasingly influence aws mdr design, assuming breach scenarios and implementing continuous verification rather than perimeter-based security models. Moreover, the convergence of security operations and observability platforms creates unified tools managing both performance and security concerns from single interfaces.
Finally, regulatory requirements continue expanding globally, with data sovereignty and privacy protection becoming universal expectations rather than regional exceptions. Consequently, aws mdr providers must navigate increasingly complex compliance landscapes whilst maintaining operational effectiveness across jurisdictions.
Implementing comprehensive aws mdr services represents a critical step towards robust cloud security, combining advanced technology with expert oversight to protect business-critical infrastructure. Nevertheless, European organisations must carefully consider data sovereignty and compliance requirements when selecting security solutions. For businesses seeking GDPR-compliant infrastructure with guaranteed European data residency, vBoxx delivers secure cloud services from ISO 27001-certified Netherlands data centres, ensuring your data remains protected under European jurisdiction whilst maintaining the flexibility and performance modern businesses demand.