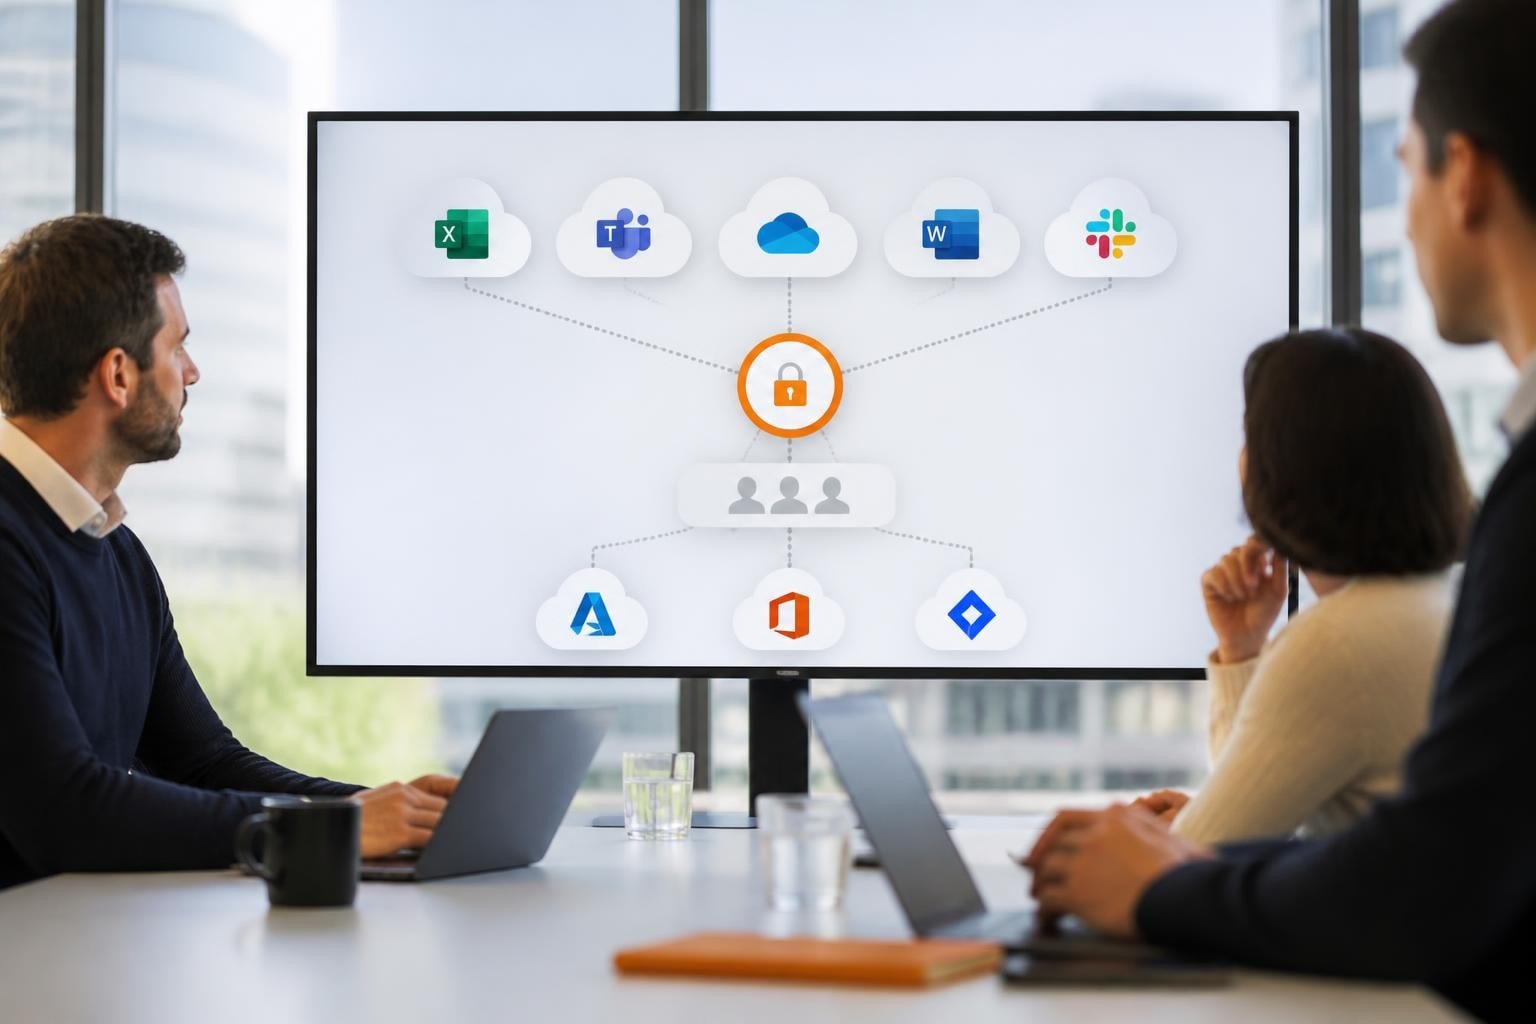
Microsoft cloud apps have fundamentally transformed how businesses operate, communicate, and secure their digital assets. From Microsoft 365 and Teams to OneDrive and SharePoint, these applications deliver productivity tools that scale from small teams to global enterprises. Nevertheless, the shift to cloud-based applications introduces new security, governance, and compliance challenges that organisations must address proactively. Therefore, understanding how microsoft cloud apps integrate within your infrastructure, how to manage permissions effectively, and how to protect sensitive data becomes essential for any business pursuing digital transformation in 2026.
Understanding the Microsoft Cloud Apps Ecosystem
The microsoft cloud apps portfolio extends far beyond the familiar Office applications. Microsoft 365 encompasses email through Exchange Online, collaborative workspaces via Teams and SharePoint, cloud storage with OneDrive, and business intelligence tools such as Power BI. Furthermore, the Azure ecosystem adds application hosting, databases, AI services, and development platforms. In addition, thousands of third-party applications integrate with Microsoft's identity and data services through OAuth and APIs, creating a complex web of permissions and data flows.
Core Microsoft Cloud Applications
Microsoft's first-party cloud apps form the foundation of most enterprise digital workplaces. Exchange Online manages email, calendaring, and contacts for millions of organisations worldwide. Teams provides chat, video conferencing, and collaboration channels that replaced separate tools for many businesses. Moreover, SharePoint Online delivers document management and intranet capabilities, while OneDrive offers personal cloud storage linked to corporate identity.
| Application | Primary Function | Key Integration Points |
|---|---|---|
| Exchange Online | Email & calendar | Teams, Outlook, mobile apps |
| Microsoft Teams | Collaboration & meetings | SharePoint, OneDrive, third-party apps |
| SharePoint Online | Document management | Teams, Power Platform, search |
| OneDrive for Business | Personal cloud storage | Office apps, Teams, File Explorer |
| Power Platform | Low-code automation | All M365 apps, external data sources |
These applications share a common identity layer through Microsoft Entra ID (formerly Azure Active Directory), which centralizes authentication and conditional access policies. Nevertheless, each application maintains its own permission model and data residency characteristics.
Third-Party Cloud App Integrations
Beyond Microsoft's own services, the broader microsoft cloud apps ecosystem includes thousands of third-party SaaS applications. These integrate through Microsoft Graph API, Azure AD authentication, and marketplace offerings. Furthermore, businesses typically use 50-100 distinct cloud applications across departments, creating shadow IT challenges and permission sprawl.
Third-party applications request OAuth permissions to access Microsoft resources such as email, calendar, files, or user profiles. Therefore, organisations must establish governance frameworks to evaluate, approve, and monitor these integrations. Microsoft Defender for Cloud Apps provides Cloud Access Security Broker (CASB) capabilities to discover, assess, and control third-party cloud app usage across the enterprise.
Security Challenges with Microsoft Cloud Apps
The convenience of microsoft cloud apps comes with significant security considerations. Unlike on-premises systems where perimeter security dominated, cloud applications require identity-centric security models, zero-trust architectures, and continuous monitoring. Moreover, the shared responsibility model means Microsoft secures the infrastructure whilst organisations remain responsible for data classification, access controls, and user behavior.
Permission and Consent Management
One of the most critical security challenges involves managing OAuth permissions and application consent. When users approve third-party applications, they grant access to their Microsoft 365 data, potentially creating backdoors that persist even after passwords change. Furthermore, overly permissive applications may request access to all mailboxes, all SharePoint sites, or all user profiles.
Recent academic research has highlighted these risks. A 2026 arXiv study analyzing the Microsoft 365 app ecosystem found that permission models often confuse users, leading to excessive grants that persist indefinitely. Therefore, organisations should:
- Implement admin consent workflows requiring approval for high-privilege permissions
- Regularly audit OAuth grants using Microsoft Defender for Cloud Apps or PowerShell
- Apply conditional access policies that restrict app access based on device compliance
- Educate users about permission requests and approved application catalogs
In addition, recent security incidents have prompted Microsoft to enhance governance capabilities. TechRadar reported on updates to Microsoft Defender for Cloud Apps that improve OAuth app governance and detection of suspicious permission patterns.
Data Loss Prevention and Compliance
Microsoft cloud apps handle sensitive business information ranging from customer data to intellectual property. Consequently, organisations must implement data loss prevention (DLP) policies that follow data across applications. Microsoft 365 DLP integrates with Exchange, Teams, SharePoint, and OneDrive to detect and protect sensitive information based on content patterns, labels, or metadata.
Nevertheless, DLP effectiveness depends on proper configuration and ongoing tuning. Businesses should establish classification taxonomies aligned with regulatory requirements such as GDPR, define policies that balance security with productivity, and monitor policy violations to refine rules. Furthermore, eDiscovery capabilities help organisations respond to legal holds and investigation requests whilst maintaining compliance.
For businesses prioritizing data protection compliance, understanding where microsoft cloud apps store data becomes critical. Microsoft offers regional data residency options, but many organisations seek additional sovereignty guarantees beyond what hyperscale providers offer.
Governance and Risk Management
Effective governance of microsoft cloud apps requires visibility, policy enforcement, and continuous risk assessment. Traditional IT management tools often lack the capabilities needed to secure and govern cloud-native applications. Therefore, organisations turn to Cloud Access Security Brokers (CASB), security information and event management (SIEM) platforms, and integrated Microsoft security services.
Establishing Cloud App Governance Frameworks
A comprehensive governance framework addresses application discovery, risk scoring, policy enforcement, and incident response. Microsoft Defender for Cloud Apps provides these capabilities natively for Microsoft 365 and can extend to other cloud services through API connectors or proxy-based discovery.
Key governance components include:
- Shadow IT discovery - Identifying unauthorized cloud applications through network traffic analysis or endpoint agents
- Risk assessment - Scoring applications based on compliance certifications, security features, and business criticality
- Policy creation - Defining acceptable use, access controls, and automated responses to violations
- Continuous monitoring - Analyzing user behavior, data movement, and permission changes for anomalies
- Incident response - Integrating cloud app alerts with broader security operations workflows
Moreover, governance frameworks should align with established security standards. The CIS Critical Security Controls provide prescriptive guidance applicable to cloud application security, whilst NIST cloud computing publications offer detailed technical frameworks for cloud-native architectures.
Backup and Business Continuity
Whilst microsoft cloud apps offer high availability and redundancy, they do not guarantee protection against user error, malicious deletion, or ransomware. Microsoft's retention policies have limits, and recovering data outside those windows may prove impossible. Furthermore, organisations face compliance requirements that exceed native Microsoft 365 retention capabilities.
Therefore, businesses implementing microsoft cloud apps should consider third-party backup solutions. These services provide point-in-time recovery, extended retention, and protection against ransomware that may spread through synchronized folders. For organisations using Microsoft 365, european backup solutions hosted outside US jurisdiction offer additional data sovereignty benefits whilst ensuring GDPR compliance.
| Risk Scenario | Native M365 Protection | Third-Party Backup Benefit |
|---|---|---|
| Accidental deletion | 93-day retention | Unlimited retention periods |
| Ransomware encryption | Limited versioning | Point-in-time restore |
| Malicious insider | Audit logs only | Immutable backup copies |
| Compliance gaps | Basic legal hold | Granular eDiscovery |
| Service outage | Microsoft redundancy | Independent recovery option |
In addition, businesses should test recovery procedures regularly. Cloud backup solutions prove their value only when recovery processes work reliably under pressure.
Integration Strategies for Business Workflows
Microsoft cloud apps deliver maximum value when integrated thoughtfully into business processes. Rather than treating each application as a standalone tool, organisations should design workflows that span multiple services, automate repetitive tasks, and surface information where teams need it. Nevertheless, integration complexity can overwhelm IT departments without clear strategies and governance.
Automation with Power Platform
Microsoft Power Platform enables business users to create integrations without extensive coding. Power Automate connects microsoft cloud apps through pre-built connectors, triggering actions based on events such as new emails, form submissions, or file uploads. Furthermore, Power Apps allows custom interfaces that aggregate data from multiple sources into unified business applications.
Common automation scenarios include:
- Routing approval requests from SharePoint to Teams with Power Automate flows
- Creating custom dashboards in Power BI that combine Microsoft 365 and external data
- Building intake forms with Power Apps that populate SharePoint lists and notify stakeholders
- Synchronizing customer data between Dynamics 365 and third-party CRM platforms
- Generating documents automatically based on templates and database information
These integrations reduce manual work and improve data consistency. Nevertheless, organisations should establish governance policies for citizen development to prevent fragmentation and ensure solutions meet security requirements.
API-First Integration Architecture
For more complex requirements, businesses leverage Microsoft Graph API to build custom integrations with microsoft cloud apps. Graph API provides a unified endpoint for accessing data across Exchange, Teams, SharePoint, OneDrive, and Azure services. Moreover, it supports both read operations for reporting and write operations for automation.
Development teams can create applications that analyze email patterns for sales insights, automate team provisioning based on HR systems, or surface relevant documents within custom portals. Furthermore, Graph API supports webhooks for real-time notifications, reducing the need for constant polling.
Security considerations remain paramount when building custom integrations. Applications should request minimum necessary permissions, implement certificate-based authentication rather than password-based flows, and log all data access for audit purposes. In addition, organisations should register applications through Azure AD to maintain centralized visibility and control.
Compliance and Data Sovereignty Considerations
For European businesses, data protection compliance extends beyond GDPR technical requirements to include data sovereignty and jurisdiction concerns. Microsoft cloud apps store data in regional datacenters, but the US CLOUD Act potentially grants American authorities access to data controlled by US companies regardless of storage location. Therefore, organisations in regulated industries or those handling sensitive information increasingly evaluate European alternatives.
Regional Data Residency Options
Microsoft offers data residency commitments through its Multi-Geo capabilities, allowing organisations to specify storage locations for Exchange, SharePoint, OneDrive, and Teams data. Nevertheless, metadata, telemetry, and some service operations may still route through US-based infrastructure. Furthermore, IT Pro recently reported on Microsoft's expanding marketplace for cloud and AI solutions, highlighting the increasing complexity of data flows in modern cloud environments.
Organisations requiring absolute data sovereignty should consider platforms operated by European entities outside US jurisdiction. vBoxxConnect provides an alternative approach, delivering integrated email, calendar, tasks, and video conferencing hosted exclusively in ISO 27001-certified Dutch datacenters, combining Microsoft-like functionality with European data sovereignty guarantees.
Sector-Specific Compliance Requirements
Different industries face unique compliance obligations when adopting microsoft cloud apps. Financial services must address DORA resilience requirements, healthcare organisations navigate HIPAA constraints, and energy sector businesses follow frameworks such as the Department of Energy Cloud Cybersecurity Profile. Moreover, public sector organizations often face additional restrictions on data location and vendor nationality.
These requirements influence not only which microsoft cloud apps organisations can adopt but also how they configure security controls, retention policies, and access restrictions. Therefore, compliance teams should participate early in cloud adoption planning to identify gaps and establish compliant configurations before deployment.
Performance Optimization and User Experience
Beyond security and compliance, organisations must ensure microsoft cloud apps deliver excellent performance and user experience. Slow applications frustrate users and drive shadow IT adoption as individuals seek faster alternatives. Furthermore, poor performance often indicates configuration issues, network constraints, or inappropriate usage patterns that waste resources.
Network and Connectivity Optimization
Microsoft cloud apps perform best with direct internet connectivity rather than routing through central VPN concentrators. Therefore, organisations increasingly adopt SD-WAN solutions or split-tunnel VPN configurations that send Microsoft 365 traffic directly to Microsoft's edge network. In addition, Microsoft publishes IP ranges and URLs that organisations should exempt from SSL inspection to prevent performance degradation and certificate errors.
Network teams should monitor key performance indicators such as latency to Exchange Online, packet loss on Teams video calls, and SharePoint upload speeds. Moreover, Microsoft provides built-in analytics through the Microsoft 365 admin center showing service health, usage patterns, and connectivity quality for different locations.
Adoption and Change Management
Technical excellence means little if users resist adopting microsoft cloud apps. Successful deployments combine technical implementation with comprehensive change management addressing training, communication, and executive sponsorship. Furthermore, organisations should identify champions within departments who can advocate for new tools and provide peer support.
Effective adoption strategies include:
- Phased rollouts starting with willing pilot groups
- Use case documentation showing how apps solve real business problems
- Regular training sessions covering both basic features and advanced capabilities
- Executive usage and visible support from leadership
- Feedback mechanisms allowing users to report issues and suggest improvements
In addition, monitoring adoption metrics helps identify departments or workflows where uptake lags. Addressing specific concerns through targeted support prevents pockets of resistance from undermining broader transformation initiatives.
Future Trends in Microsoft Cloud Apps
The microsoft cloud apps landscape continues evolving rapidly, with artificial intelligence, enhanced security capabilities, and deeper integrations reshaping what organisations can accomplish. Microsoft Copilot brings generative AI into familiar applications, potentially transforming how knowledge workers draft documents, analyze data, and find information. Nevertheless, these capabilities introduce new governance challenges around AI accuracy, data privacy, and appropriate use policies.
Furthermore, Microsoft continues strengthening security integrations across its stack. The convergence of Microsoft Defender services into a unified platform provides correlation across endpoints, email, cloud apps, and identity signals. Therefore, organisations investing in microsoft cloud apps benefit from an increasingly cohesive security ecosystem that detects sophisticated attacks spanning multiple vectors.
Looking ahead, expect continued emphasis on zero-trust architectures, where every access request requires verification regardless of network location. Moreover, sustainability metrics will gain importance as organisations measure the carbon footprint of their digital operations and seek green hosting options that reduce environmental impact.
Microsoft cloud apps offer powerful capabilities that can transform business operations, yet they require careful governance, security controls, and integration planning to deliver sustainable value. European businesses face additional considerations around data sovereignty, GDPR compliance, and jurisdiction beyond what hyperscale US providers typically address. vBoxx provides European-operated alternatives with comparable functionality but full sovereignty, hosting secure collaboration, storage, and communication tools exclusively in ISO 27001-certified Dutch datacenters outside US legal reach. Whether enhancing existing microsoft cloud apps with European backup and security layers or exploring sovereignty-first alternatives, organisations benefit from expert guidance through the complexities of modern cloud adoption.