Cloud privacy and security represent critical priorities for European businesses navigating an increasingly complex digital landscape in 2026. As organizations migrate workloads to cloud infrastructure, the intersection of data protection, regulatory compliance, and operational resilience demands careful attention. Furthermore, the evolving threat landscape documented in ENISA's 2024 Threat Landscape report highlights sophisticated attack vectors targeting cloud environments, making robust security architecture not merely advisable but essential. Therefore, understanding how to safeguard sensitive information whilst maintaining operational agility has become a defining challenge for modern enterprises.
Understanding the Cloud Privacy and Security Landscape
The fundamental challenge of cloud privacy and security lies in balancing convenience with control. Nevertheless, organizations must recognize that cloud adoption inherently introduces shared responsibility between provider and customer.
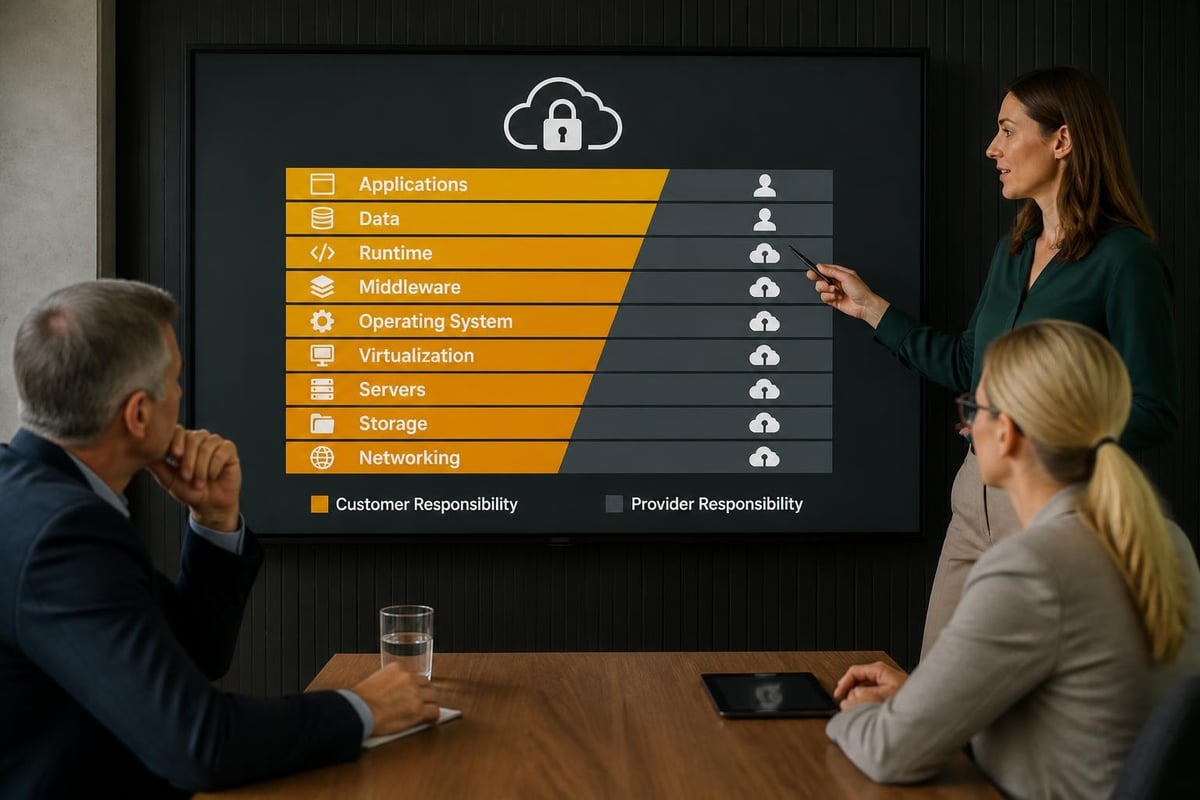
The Shared Responsibility Model
Cloud service providers manage infrastructure security, including physical data centres, network architecture, and hypervisor integrity. In addition, customers retain responsibility for application security, access controls, data classification, and encryption key management. This division creates potential gaps where misunderstandings lead to vulnerabilities.
Moreover, different service models shift responsibility boundaries:
- Infrastructure as a Service (IaaS): Customers control operating systems, applications, and data
- Platform as a Service (PaaS): Provider manages runtime environments; customers secure applications
- Software as a Service (SaaS): Provider handles most security; customers manage access and configuration
Furthermore, research published through IEEE Xplore demonstrates that misconfiguration remains the leading cause of cloud breaches, underscoring the importance of clarity in responsibility allocation.
European Data Sovereignty Considerations
For European businesses, data sovereignty has emerged as a non-negotiable requirement. The US CLOUD Act permits American authorities to compel disclosure of data held by US companies regardless of physical storage location. Therefore, selecting providers operating under European jurisdiction provides meaningful protection against extraterritorial access requests.
Additionally, GDPR Article 48 restricts data transfers to third countries unless proper legal mechanisms exist. Consequently, hosting data within ISO 27001-certified facilities in jurisdictions like the Netherlands offers both compliance assurance and operational transparency.
Essential Technical Controls for Cloud Privacy and Security
Technical safeguards form the foundation of effective cloud privacy and security strategies. Nevertheless, implementation requires careful planning and ongoing maintenance.
Encryption at Multiple Layers
Encryption protects data confidentiality across three critical states:
| Encryption State | Purpose | Implementation |
|---|---|---|
| At rest | Protects stored data from unauthorized access | AES-256 encryption of storage volumes and databases |
| In transit | Secures data moving between systems | TLS 1.3 for network communications |
| In use | Shields data during processing | Confidential computing with encrypted memory |
Furthermore, effective key management separates encryption keys from encrypted data. Therefore, organizations should implement hardware security modules (HSMs) or dedicated key management services that enforce strict access policies.
Moreover, client-side encryption ensures that sensitive data remains encrypted before leaving organizational control. This approach proves particularly valuable for zero-knowledge architectures where even the service provider cannot access plaintext data.
Identity and Access Management
Robust identity controls prevent unauthorized access whilst enabling legitimate users. In addition, NIST guidance on cloud security emphasizes the importance of identity as the new security perimeter in cloud environments.
Essential IAM components include:
- Multi-factor authentication (MFA) requiring multiple proof factors
- Role-based access control (RBAC) granting minimum necessary privileges
- Just-in-time access providing temporary elevation only when needed
- Continuous authentication reassessing trust throughout sessions
- Privileged access management monitoring and controlling administrative accounts
Nevertheless, identity alone proves insufficient. Therefore, organizations should implement attribute-based access control (ABAC) that considers context such as device health, location, and time of access. Furthermore, zero-trust architectures assume breach and verify every access request regardless of network location.
Network Security and Segmentation
Network controls limit lateral movement and contain potential breaches. Moreover, micro-segmentation creates granular boundaries between workloads, preventing attackers from pivoting across systems.
Effective network strategies combine:
- Virtual private clouds (VPCs) with private subnets for sensitive resources
- Network access control lists (NACLs) filtering traffic at subnet boundaries
- Security groups acting as instance-level firewalls
- Web application firewalls (WAFs) protecting against OWASP Top Ten vulnerabilities
- Distributed denial-of-service (DDoS) mitigation services
In addition, implementing service mesh architectures provides encrypted service-to-service communication with fine-grained policy enforcement. Therefore, organizations gain both security and observability benefits.
Compliance and Governance Frameworks
Regulatory compliance drives cloud privacy and security requirements for European organizations. Nevertheless, frameworks provide valuable structure beyond mere regulatory obligation.
GDPR and Data Protection Requirements
The General Data Protection Regulation establishes comprehensive requirements for personal data processing. Furthermore, cloud deployments must address specific GDPR principles:
| GDPR Principle | Cloud Implementation |
|---|---|
| Lawfulness | Document legal basis for processing; obtain consent where required |
| Purpose limitation | Define retention policies; implement automated deletion |
| Data minimization | Collect only necessary data; use pseudonymization |
| Accuracy | Enable data subject access and correction workflows |
| Storage limitation | Enforce retention schedules; archive or delete expired data |
| Integrity and confidentiality | Apply encryption, access controls, and audit logging |
| Accountability | Maintain processing records; conduct impact assessments |
Moreover, Article 32 specifically requires "appropriate technical and organisational measures" considering the state of the art. Therefore, implementing modern encryption, access controls, and monitoring demonstrates due diligence.
In addition, organizations must carefully assess data processor agreements. Cloud providers acting as processors must offer sufficient guarantees and comply with controller instructions. Consequently, contract terms should clearly define security obligations, breach notification timelines, and audit rights.
ISO 27001 and Security Management
ISO 27001 provides a systematic framework for information security management. Nevertheless, certification requires ongoing commitment rather than one-time implementation.
The standard's risk-based approach aligns well with cloud privacy and security needs. Furthermore, organizations must:
- Establish context by defining scope and stakeholder requirements
- Assess risks through systematic threat identification and impact analysis
- Select controls from Annex A based on risk treatment decisions
- Implement measures with documented procedures and responsibilities
- Monitor performance using metrics and management review
- Continually improve through corrective actions and lessons learned
Additionally, ISO 27017 extends ISO 27001 specifically for cloud services, addressing cloud-specific controls such as virtual machine hardening, cloud service customer responsibilities, and resource isolation. Therefore, organizations seeking comprehensive cloud security should consider both standards together.
Industry-Specific Requirements
Beyond horizontal regulations, sector-specific frameworks impose additional obligations. For instance, financial services organizations must comply with requirements from the European Banking Authority, whilst healthcare providers navigate medical device regulations and patient confidentiality rules.
Moreover, the proposed EU Cyber Resilience Act will mandate security requirements for products with digital elements. Consequently, organizations developing or deploying cloud-based software must prepare for lifecycle security obligations including vulnerability disclosure and security update management.
Operational Security Practices
Implementing cloud privacy and security requires continuous operational discipline. Nevertheless, organizations often underestimate the ongoing effort required to maintain security posture.
Configuration Management and Hardening
The SANS Institute's multicloud research consistently identifies misconfiguration as a leading vulnerability source. Therefore, organizations should implement configuration management practices including:
- Baseline hardening templates following vendor and framework guidance
- Infrastructure as code enabling version control and peer review
- Automated compliance scanning detecting drift from approved configurations
- Immutable infrastructure replacing rather than patching components
- Change management workflows requiring approval for production modifications
Furthermore, the Cloud Security Alliance publishes consensus guidance on secure configuration across major cloud platforms. In addition, tools such as cloud security posture management (CSPM) solutions continuously assess configuration against industry benchmarks.
Logging, Monitoring, and Incident Response
Visibility enables detection and response to security events. Moreover, comprehensive logging supports forensic investigation, compliance auditing, and operational troubleshooting.
Essential monitoring capabilities include:
- Centralized log aggregation collecting events from all cloud resources
- Security information and event management (SIEM) correlating events and generating alerts
- User and entity behavior analytics (UEBA) detecting anomalous patterns
- File integrity monitoring identifying unauthorized changes
- Cloud workload protection platforms providing runtime threat detection
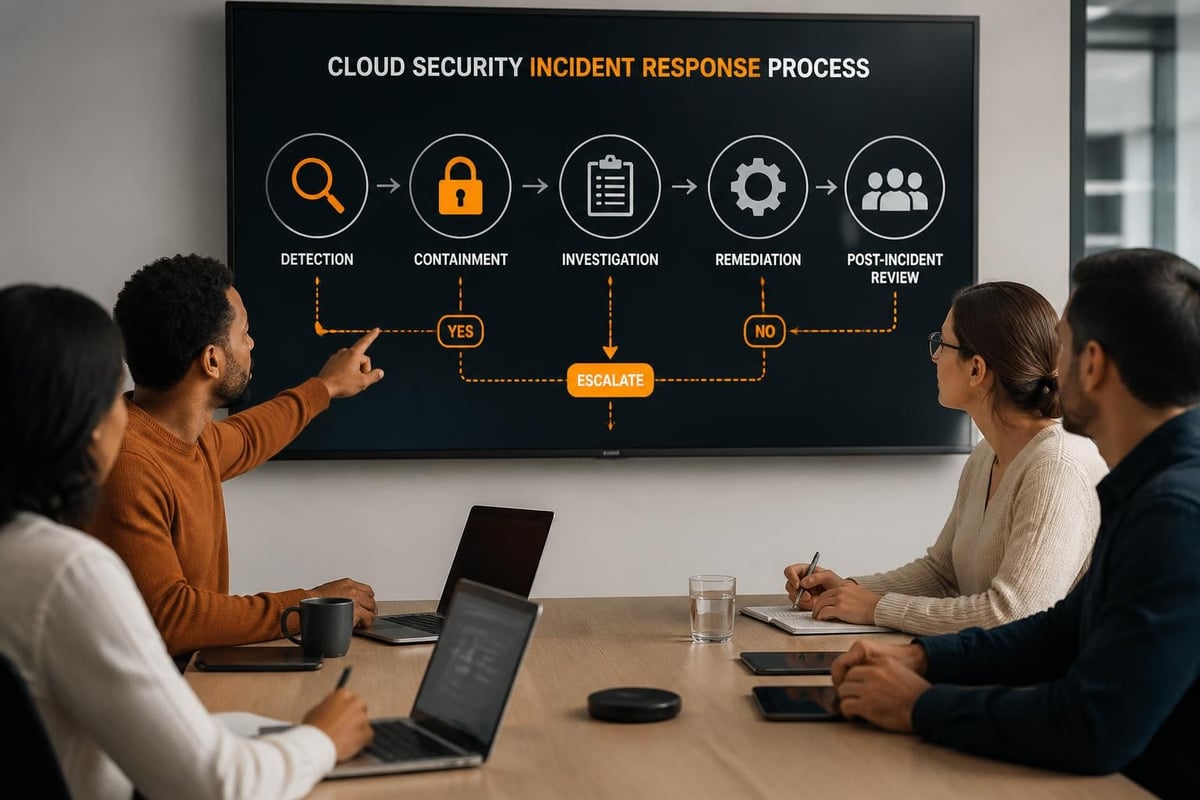
Nevertheless, monitoring alone proves insufficient without incident response capabilities. Therefore, organizations should develop and regularly test incident response plans that address cloud-specific scenarios such as compromised credentials, cryptomining attacks, and data exfiltration.
In addition, CISA directives provide operational guidance on vulnerability management, known exploited vulnerabilities, and cyber hygiene practices applicable to cloud environments.
Backup and Disaster Recovery
Data loss represents a critical privacy and security incident. Furthermore, ransomware attacks increasingly target backup systems to maximize pressure on victims.
Effective backup strategies implement the 3-2-1 rule: three copies of data, on two different media types, with one copy off-site. Moreover, cloud-native backup should address:
- Automated backup scheduling ensuring consistent protection without manual intervention
- Version retention enabling recovery from specific points in time
- Geographic redundancy protecting against regional outages or disasters
- Immutable backups preventing modification or deletion during retention periods
- Regular recovery testing validating that backups can actually be restored
Additionally, for organizations using SaaS platforms such as Microsoft 365 or Google Workspace, native retention features may prove insufficient. Therefore, dedicated cloud-to-cloud backup services provide additional protection against accidental deletion, retention policy gaps, and malicious insider threats.
Selecting Cloud Providers and Services
Provider selection directly impacts cloud privacy and security outcomes. Nevertheless, evaluation requires looking beyond marketing claims to examine actual practices and certifications.
Evaluation Criteria
When assessing potential cloud providers, organizations should systematically evaluate:
| Criterion | Key Considerations |
|---|---|
| Data location | Physical location of data centres; data residency guarantees |
| Legal jurisdiction | Corporate structure; applicable laws and government access provisions |
| Certifications | ISO 27001, SOC 2, industry-specific attestations |
| Encryption | Default encryption; key management options; support for customer-managed keys |
| Access controls | IAM capabilities; MFA support; privilege management features |
| Network security | Isolation mechanisms; DDoS protection; private connectivity options |
| Compliance support | GDPR processing agreements; audit reports; compliance documentation |
| Incident response | Breach notification procedures; forensic support capabilities |
| Transparency | Security documentation quality; vulnerability disclosure practices |
Furthermore, organizations should request and review security documentation including architecture diagrams, penetration test summaries, and third-party audit reports. In addition, contractual terms should clearly define security responsibilities, service level agreements, and data handling procedures.
European Cloud Providers and Data Sovereignty
For organizations prioritizing data sovereignty, European cloud providers offer jurisdictional protection against extraterritorial data access requests. Moreover, providers operating infrastructure in European Economic Area member states remain subject exclusively to EU law.
vBoxxCloud exemplifies this approach, operating ISO 27001-certified data centres in the Netherlands with GDPR-compliant business cloud storage and 256-bit AES encryption. As a European company outside the reach of the US CLOUD Act, such providers eliminate concerns about foreign government access whilst maintaining compliance with EU regulations. Furthermore, these platforms often include eIDAS-compliant digital signing, team collaboration features, and integrated AI capabilities alongside their core storage and security functions.
Nevertheless, even when selecting European providers, organizations should conduct thorough due diligence. Therefore, verify certifications, review processing agreements, and assess the provider's security track record and incident history.
Emerging Trends in Cloud Privacy and Security
The cloud privacy and security landscape continues evolving rapidly. Moreover, emerging technologies and regulatory developments will shape requirements throughout 2026 and beyond.
Confidential Computing
Confidential computing protects data during processing through hardware-based trusted execution environments. Furthermore, this technology addresses the final frontier of encryption by securing data in use.
Modern processors from Intel, AMD, and ARM include secure enclaves that isolate code and data from the host operating system and hypervisor. Therefore, even cloud provider administrators cannot access data processed within these protected environments. In addition, attestation mechanisms enable verification that workloads run in genuine secure enclaves.
Nevertheless, confidential computing introduces complexity and performance overhead. Consequently, organizations should prioritize its use for processing highly sensitive data such as personal information, financial records, and confidential business data.
Zero Trust Architecture
Zero trust fundamentally reimagines network security by eliminating implicit trust. Moreover, this approach proves particularly relevant for cloud environments where traditional network perimeters dissolve.
Core zero trust principles include:
- Verify explicitly using all available data points for authentication decisions
- Use least privilege access granting minimum necessary permissions
- Assume breach designing systems to limit blast radius and detect compromises
Furthermore, implementing zero trust requires coordinating identity, device, network, application, and data controls. Therefore, organizations typically adopt zero trust incrementally, beginning with high-value assets and gradually expanding coverage.
Privacy-Enhancing Technologies
Privacy-enhancing technologies enable data analysis whilst preserving confidentiality. Moreover, techniques such as differential privacy, homomorphic encryption, and secure multi-party computation allow valuable insights from sensitive data without exposing individual records.
In addition, federated learning trains machine learning models across distributed datasets without centralizing data. Therefore, organizations can collaborate on AI initiatives whilst maintaining data sovereignty and privacy compliance.
Nevertheless, these technologies remain computationally intensive and complex to implement. Consequently, adoption currently focuses on specific high-value use cases rather than general-purpose deployment.
Regulatory Evolution
European cloud regulation continues developing beyond GDPR. Furthermore, proposed frameworks will introduce additional requirements:
- Digital Operational Resilience Act (DORA) mandating ICT risk management for financial entities
- NIS2 Directive expanding cybersecurity requirements across critical sectors
- EU Cloud Certification Scheme providing standardized security assurance levels
- Data Act establishing rules for data access and portability
Moreover, research published via arXiv on cloud security certification explores quantifiable metrics for evaluating cloud security posture. Therefore, expect increasing emphasis on measurable, auditable security controls rather than subjective assessments.
Practical Implementation Strategies
Implementing comprehensive cloud privacy and security requires systematic planning and phased execution. Nevertheless, organizations can begin with foundational steps and progressively enhance capabilities.
Assessment and Gap Analysis
Begin by documenting current cloud usage, data flows, and existing controls. Furthermore, identify shadow IT through network monitoring and user surveys to understand the complete cloud footprint.
Next, compare current practices against regulatory requirements, industry frameworks, and internal policies. Therefore, create a prioritized gap list considering both risk severity and implementation complexity.
In addition, engage stakeholders across IT, legal, compliance, and business units. Moreover, securing executive sponsorship proves essential for obtaining necessary resources and driving organizational change.
Phased Rollout Approach
Rather than attempting comprehensive implementation simultaneously, adopt a phased approach:
Phase 1: Foundation (months 1-3)
- Implement MFA across all cloud services
- Enable encryption at rest and in transit
- Establish centralized logging and basic monitoring
- Document cloud inventory and data flows
Phase 2: Enhanced Controls (months 4-6)
- Deploy privilege management and RBAC
- Implement network segmentation and security groups
- Establish configuration management and compliance scanning
- Develop incident response procedures
Phase 3: Advanced Capabilities (months 7-12)
- Integrate SIEM and behavioral analytics
- Implement automated compliance reporting
- Deploy workload protection and runtime security
- Establish backup and disaster recovery procedures
Phase 4: Optimization (ongoing)
- Continuously improve based on threat intelligence
- Expand zero trust implementation
- Evaluate emerging technologies
- Conduct regular security assessments and penetration tests
Furthermore, each phase should include training and awareness activities ensuring that technical controls align with user understanding and organizational culture.
Building Security Culture
Technology alone cannot ensure cloud privacy and security. Moreover, human factors significantly influence security outcomes through both intentional actions and inadvertent mistakes.
Therefore, organizations should invest in security awareness programmes addressing:
- Phishing recognition helping users identify social engineering attempts
- Data classification ensuring appropriate handling of sensitive information
- Secure configuration educating administrators on hardening best practices
- Incident reporting encouraging prompt disclosure without fear of punishment
- Privacy principles building understanding of GDPR requirements and individual rights
In addition, integrate security considerations into existing processes rather than creating parallel workflows. Consequently, security becomes embedded in normal operations rather than perceived as burdensome overhead.
Cloud privacy and security demand ongoing attention as threats evolve and regulatory expectations increase. Nevertheless, European businesses can achieve robust protection through systematic implementation of technical controls, compliance frameworks, and operational practices whilst selecting providers that prioritize data sovereignty and jurisdictional transparency. vBoxx supports this journey with ISO 27001-certified infrastructure, GDPR-compliant cloud solutions, and European hosting free from extraterritorial access risks, combining secure storage, communication, and password management with expert guidance and migration support. Therefore, organizations seeking comprehensive cloud privacy and security can build their digital infrastructure on a foundation designed for European regulatory requirements and business continuity.