Amazon Web Services (AWS) powers millions of workloads globally, yet European businesses face unique challenges when using its infrastructure for GDPR compliance aws implementations. Furthermore, understanding the division of responsibilities, data transfer mechanisms, and technical safeguards becomes critical when processing personal data of EU citizens on a non-European cloud platform. This guide examines the essential elements of achieving and maintaining GDPR compliance aws configurations, from contractual frameworks to encryption standards, helping organisations navigate the complex intersection of European data protection law and American cloud infrastructure.
Understanding the Shared Responsibility Model for GDPR
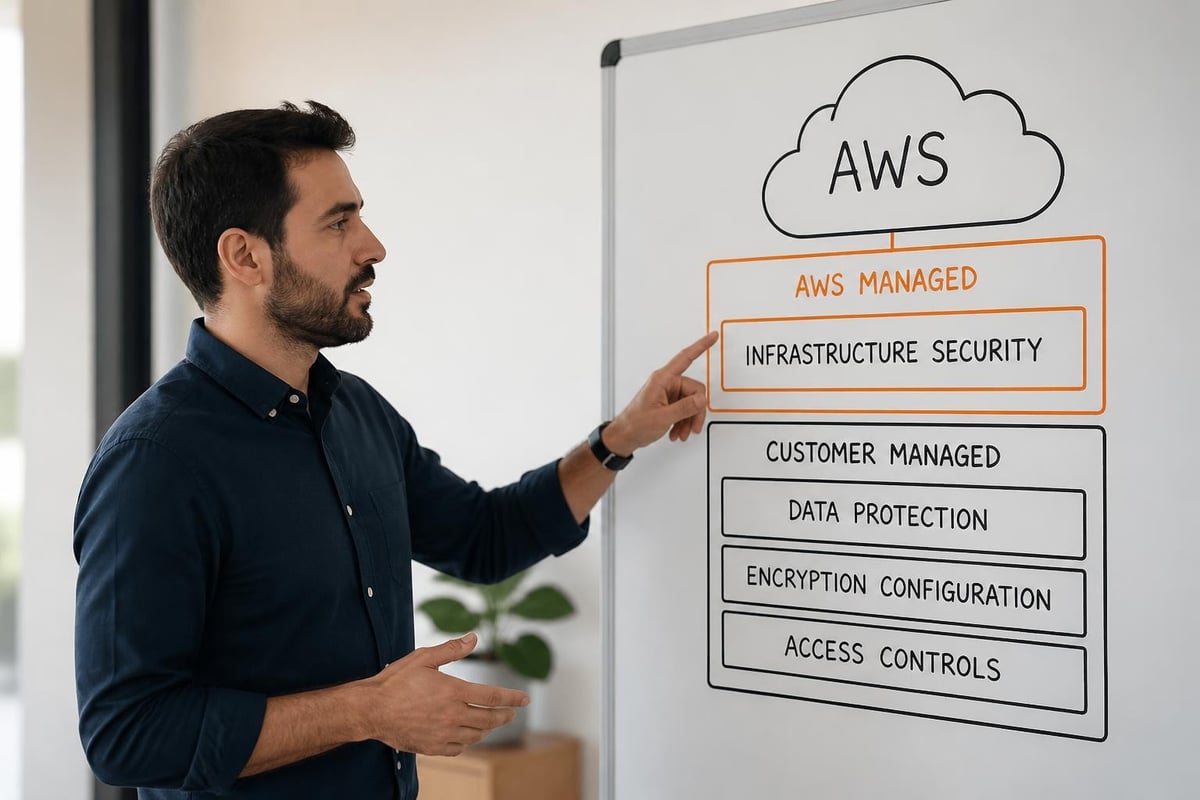
When implementing gdpr compliance aws strategies, businesses must first grasp the fundamental division of responsibilities between AWS as infrastructure provider and the customer as data controller or processor. AWS operates under a shared responsibility model that clearly delineates which GDPR obligations fall to each party, preventing dangerous gaps in compliance coverage.
AWS assumes responsibility for security of the cloud, encompassing the physical infrastructure, hardware, software, networking, and facilities that run AWS services. Consequently, AWS maintains ISO 27001 certification, SOC reports, and numerous other compliance attestations for its infrastructure layer. Nevertheless, this does not automatically make your workloads GDPR-compliant.
Customer Responsibilities Under the Model
Customers retain full responsibility for security in the cloud, which includes nearly all GDPR-specific obligations:
- Data classification and governance across all AWS services used
- Access management through IAM policies and identity federation
- Encryption configuration for data at rest and in transit
- Network security via VPCs, security groups, and network ACLs
- Data subject rights fulfilment including access, erasure, and portability
- Breach notification procedures and incident response planning
Moreover, customers must configure AWS services correctly to meet GDPR requirements. Therefore, simply hosting on AWS infrastructure does not guarantee compliance; the implementation details matter significantly. In addition, organisations must maintain comprehensive documentation demonstrating their technical and organisational measures.
Data Residency and International Transfer Mechanisms
One of the most critical aspects of gdpr compliance aws involves managing where personal data physically resides and how it crosses borders. Furthermore, the Schrems II ruling invalidated the EU-US Privacy Shield, requiring additional scrutiny of transfers to AWS regions outside the European Economic Area.
Selecting Appropriate AWS Regions
AWS operates multiple regions within the EU, including Frankfurt, Ireland, Paris, Stockholm, Milan, and Spain. Choosing these regions for primary data storage addresses the first layer of GDPR data residency concerns. Nevertheless, simply selecting an EU region does not eliminate all transfer risks, as certain AWS services may route data through or store metadata in non-EU locations.
Subsequently, businesses must audit each AWS service to understand its data flows. For instance, some global services like CloudFront or Route 53 operate across multiple regions by design. In addition, support interactions and service logs may transfer data outside the EU unless specifically configured otherwise.
| AWS Service Type | Default Behaviour | GDPR Consideration |
|---|---|---|
| EC2, RDS, S3 | Data stays in selected region | Choose EU regions only |
| CloudFront | Global edge network | Configure geo-restrictions |
| IAM | Global service | Metadata may leave EU |
| CloudTrail | Region-specific logs | Configure EU-only logging |
| Support | Global support teams | May involve data transfers |
Implementing Standard Contractual Clauses
AWS offers Standard Contractual Clauses (SCCs) as a legal mechanism for data transfers to non-EU regions. These contractual safeguards, updated in 2021, establish obligations for both data exporters (customers) and importers (AWS) to protect personal data transferred outside the EEA.
However, SCCs alone may not suffice following the Schrems II judgment. Therefore, organisations must conduct Transfer Impact Assessments (TIAs) evaluating whether local laws in the destination country might undermine SCC protections. The EDPB provides guidance on conducting these assessments, particularly regarding US government access to data under laws like FISA 702 and Executive Order 12333.
Technical and Organisational Measures
Achieving gdpr compliance aws requires implementing robust technical controls beyond contractual frameworks. Furthermore, GDPR Article 32 mandates appropriate security measures considering the state of the art, implementation costs, and the risks to data subjects' rights and freedoms.
Encryption at Rest and in Transit
Encryption serves as a cornerstone of GDPR's security requirements. AWS provides multiple encryption options:
At-rest encryption:
- S3 offers server-side encryption with AWS-managed keys (SSE-S3), AWS KMS keys (SSE-KMS), or customer-provided keys (SSE-C)
- RDS and EBS support encryption using AWS KMS with customer-managed keys
- DynamoDB enables encryption by default with AWS-owned or customer-managed KMS keys
In-transit encryption:
- TLS/SSL for all API communications
- VPN connections for hybrid architectures
- AWS Certificate Manager for managing SSL/TLS certificates
Nevertheless, encryption effectiveness depends on proper key management. Therefore, using AWS Key Management Service (KMS) with customer-managed keys provides greater control and supports key rotation policies required for compliance. In addition, segregating keys by data classification ensures that highly sensitive personal data receives stronger protection.
Access Control and Identity Management
GDPR Article 32(1) requires measures to ensure ongoing confidentiality, particularly restricting access to personal data. Moreover, implementing least-privilege access through AWS Identity and Access Management (IAM) becomes essential:
- Create granular IAM policies limiting access to specific resources and actions
- Implement multi-factor authentication (MFA) for all privileged accounts
- Use IAM roles instead of long-term credentials wherever possible
- Enable AWS CloudTrail for comprehensive audit logging of all API calls
- Configure Amazon GuardDuty for threat detection and anomaly monitoring
Furthermore, integrating AWS with existing identity providers through SAML 2.0 or OpenID Connect centralises authentication management. Subsequently, this approach facilitates compliance with GDPR's accountability principle by maintaining consistent identity and access records.
Data Processing Agreements and Controller-Processor Relationships
GDPR Article 28 requires written contracts between data controllers and processors specifying processing instructions, security measures, and sub-processor arrangements. Consequently, AWS provides the AWS Data Processing Addendum (DPA) automatically incorporated into customer agreements for services processing personal data.
Key Elements of the AWS DPA
The AWS DPA addresses several critical GDPR requirements:
- Processing instructions: AWS processes personal data only according to customer instructions through the AWS console, APIs, or SDKs
- Confidentiality commitments: AWS personnel accessing customer data undergo confidentiality training and obligations
- Security measures: AWS implements technical and organisational measures detailed in security whitepapers
- Sub-processor notifications: AWS maintains a list of sub-processors and provides notification mechanisms for changes
- Data subject rights assistance: AWS provides tools and features enabling customers to fulfil access, rectification, and erasure requests
Nevertheless, customers retain ultimate responsibility as data controllers for ensuring their AWS configurations meet GDPR requirements. Therefore, relying solely on AWS's DPA without implementing proper technical controls creates compliance gaps.
Logging, Monitoring, and Breach Detection
GDPR Article 33 mandates breach notification within 72 hours of becoming aware of a personal data breach. Furthermore, Article 5(2) requires demonstrating compliance through appropriate records. Subsequently, comprehensive logging and monitoring become essential components of gdpr compliance aws implementations.
Essential AWS Logging Services
| Service | Purpose | GDPR Application |
|---|---|---|
| AWS CloudTrail | API activity logging | Accountability and audit trail |
| Amazon CloudWatch | Performance and application monitoring | Anomaly detection and alerting |
| AWS Config | Resource configuration tracking | Configuration compliance verification |
| Amazon GuardDuty | Threat detection | Security incident identification |
| AWS Security Hub | Centralised security findings | Compliance posture assessment |
Moreover, configuring these services correctly requires attention to log retention policies, encryption of log data, and access controls preventing unauthorised modification. Therefore, storing CloudTrail logs in a dedicated S3 bucket with object lock and lifecycle policies ensures tamper-proof audit trails meeting GDPR's accountability requirements.
Implementing Breach Detection and Response
AWS provides numerous tools for detecting potential data breaches, yet customers must configure alerting and response procedures:
- Enable Amazon GuardDuty across all regions to detect unauthorised access attempts, compromised credentials, and unusual API activity
- Configure CloudWatch alarms for suspicious activities like failed login attempts, unusual data transfer volumes, or configuration changes
- Implement AWS Config rules monitoring compliance with security baselines and detecting configuration drift
- Establish SNS notifications routing security alerts to incident response teams
- Document incident response procedures specifying breach assessment, containment, notification, and remediation steps
In addition, regularly testing incident response procedures through tabletop exercises ensures teams can meet the 72-hour notification deadline. Furthermore, maintaining up-to-date contact information for data protection authorities and affected data subjects facilitates rapid notification when necessary.
Data Subject Rights and AWS Tools
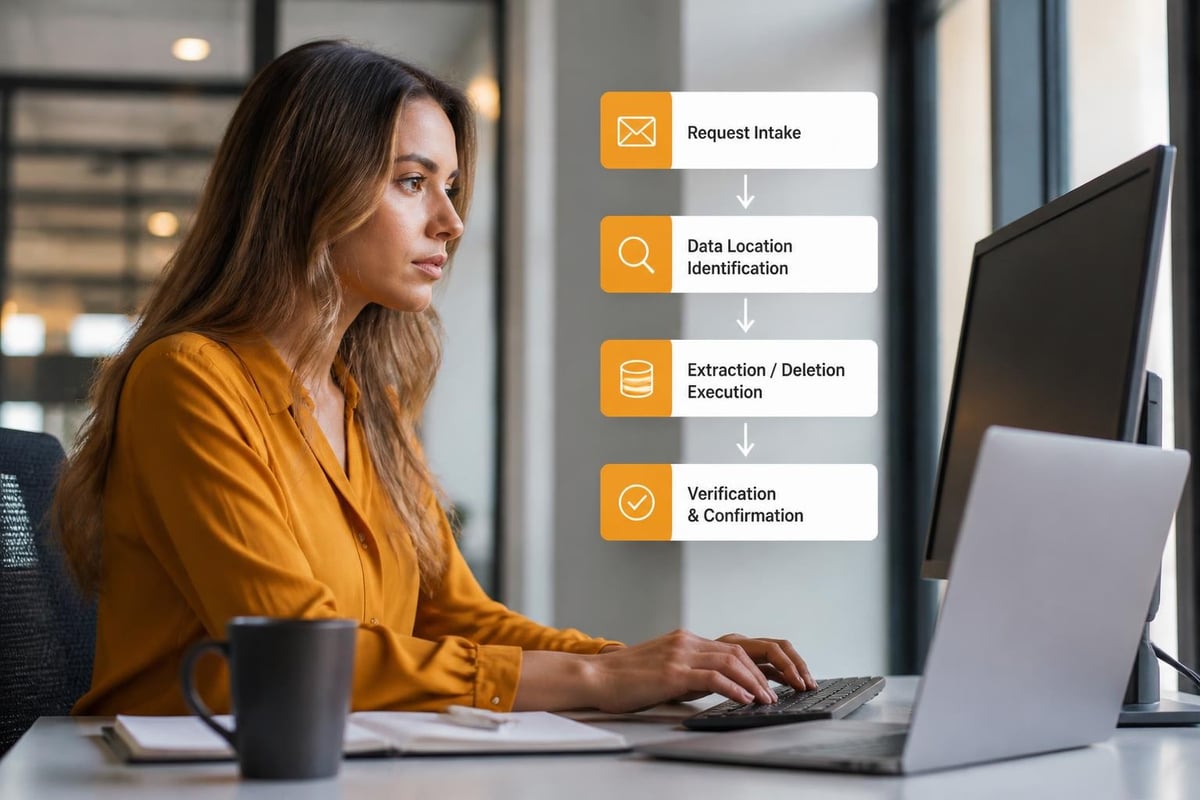
GDPR grants individuals extensive rights over their personal data, including access, rectification, erasure, restriction, portability, and objection. Consequently, organisations using AWS must implement mechanisms to efficiently fulfil these requests within the required timeframes.
Right to Access and Data Portability
AWS provides APIs and tools enabling data extraction in structured formats. For instance, S3 supports bulk export operations, RDS allows database dumps, and DynamoDB enables JSON exports. Nevertheless, organisations must maintain accurate data inventories mapping individuals to their data locations across AWS services.
Furthermore, implementing comprehensive tagging strategies helps identify personal data requiring extraction. Therefore, using resource tags indicating data classification, retention periods, and data subject identifiers facilitates rapid response to access requests.
Right to Erasure and Restriction
The "right to be forgotten" requires organisations to delete personal data under certain circumstances. AWS services support deletion through various mechanisms:
- S3 object deletion with versioning controls and lifecycle policies
- RDS row deletion through standard SQL DELETE operations
- DynamoDB item deletion via API calls or batch operations
- EBS volume deletion ensuring cryptographic erasure
Moreover, implementing soft-delete patterns with deletion flags enables compliance with both erasure requests and legal retention obligations. Subsequently, automated processes can permanently delete flagged data once retention periods expire.
Privacy by Design and Default in AWS Architectures
GDPR Article 25 requires implementing data protection measures both at the design stage and by default configuration. Furthermore, this principle applies directly to how organisations architect solutions on AWS, necessitating privacy considerations from project inception.
Minimisation and Purpose Limitation
AWS's flexible service offerings enable organisations to collect only necessary data. Therefore, implementing data minimisation involves:
- Designing database schemas excluding unnecessary personal data fields
- Configuring CloudFront to strip unnecessary headers before logging
- Using API Gateway request validation rejecting superfluous data
- Implementing Lambda functions filtering data before storage
In addition, clearly documenting processing purposes and configuring access controls ensuring data usage aligns with stated purposes demonstrates purpose limitation compliance. Moreover, separating data processing environments by purpose prevents unauthorised cross-purpose data usage.
Privacy-Enhancing Technologies
AWS supports various privacy-enhancing technologies strengthening gdpr compliance aws implementations:
- Pseudonymisation through AWS KMS envelope encryption with rotating data encryption keys
- Tokenization using AWS services or third-party solutions reducing stored personal data
- Differential privacy implementations on Amazon SageMaker for privacy-preserving analytics
- Homomorphic encryption for specific use cases requiring computation on encrypted data
Nevertheless, implementing these technologies requires careful architecture planning and may impact performance or functionality. Therefore, conducting privacy impact assessments helps balance privacy protection against operational requirements.
Vendor Lock-In and Data Portability Considerations
Whilst AWS provides extensive services for achieving GDPR compliance, organisations must consider data portability requirements extending beyond individual data subject rights. Furthermore, GDPR's accountability principle requires maintaining ability to switch providers without losing data or facing disproportionate costs.
Architectural Strategies for Portability
Implementing cloud-agnostic architectures facilitates provider independence:
- Use containerisation with Docker and Kubernetes rather than AWS-specific services where practical
- Implement infrastructure as code with Terraform or CloudFormation enabling reproducible deployments
- Prefer standard APIs over proprietary AWS services when functionality overlaps
- Maintain regular data exports to cloud-agnostic storage formats
- Document dependencies on AWS-specific services and evaluate alternatives
Moreover, organisations prioritising European data sovereignty may consider alternatives like vBoxxCloud, which offers GDPR-compliant business cloud storage with 256-bit AES encryption stored in ISO 27001-certified European data centres in the Netherlands, providing full control over data location without concerns about the US CLOUD Act.
Exit Planning and Testing
GDPR compliance extends to maintaining practical ability to migrate away from AWS. Subsequently, organisations should:
- Document all data storage locations across AWS services
- Test data extraction procedures annually ensuring completeness
- Maintain up-to-date architecture diagrams facilitating migration planning
- Evaluate migration costs preventing vendor lock-in through prohibitive switching expenses
- Establish alternative provider relationships maintaining competitive options
In addition, incorporating exit planning into business continuity procedures ensures GDPR compliance even during provider transitions or service discontinuations.
Compliance Documentation and Demonstrating Accountability
GDPR Article 5(2) establishes accountability as a core principle, requiring organisations to demonstrate compliance rather than simply claiming it. Furthermore, supervisory authorities increasingly request comprehensive documentation during investigations or audits. Therefore, maintaining thorough records of gdpr compliance aws measures becomes essential.
Essential Documentation Requirements
Organisations should maintain the following documentation:
- Data processing inventory mapping all personal data types, processing purposes, retention periods, and AWS service locations
- Technical and organisational measures documentation detailing security controls, encryption configurations, and access restrictions
- Transfer Impact Assessments for any data transfers to non-EU AWS regions
- Data Processing Agreements including the AWS DPA and any sub-processor agreements
- Privacy impact assessments for high-risk processing activities
- Incident response procedures including breach notification workflows
- Training records demonstrating staff awareness of GDPR obligations
Moreover, AWS provides extensive compliance documentation including whitepapers, audit reports, and certifications supporting customer accountability obligations. Nevertheless, customers must supplement AWS documentation with their own implementation records.
Regular Compliance Audits and Reviews
GDPR compliance requires ongoing verification rather than one-time certification. Subsequently, establishing regular audit schedules ensures continued compliance:
- Quarterly access reviews verifying least-privilege principles and removing unnecessary permissions
- Semi-annual configuration audits using AWS Config rules and Security Hub findings
- Annual privacy impact assessment updates reflecting architecture changes and new processing activities
- Continuous monitoring through CloudWatch dashboards tracking compliance metrics
- External audits by qualified assessors providing independent verification
Furthermore, integrating compliance checks into CI/CD pipelines prevents configuration drift introducing GDPR violations. Therefore, treating compliance as code rather than documentation ensures technical measures remain aligned with documented policies.
Emerging Considerations and Future-Proofing
The landscape of gdpr compliance aws continues evolving as regulatory guidance develops and AWS expands its service offerings. Moreover, several emerging considerations merit attention for organisations planning long-term AWS deployments.
AI and Automated Decision-Making
AWS machine learning services like SageMaker, Rekognition, and Comprehend introduce GDPR Article 22 considerations regarding automated decision-making. Consequently, organisations must:
- Implement human review processes for decisions significantly affecting individuals
- Maintain explainability documenting how AI models reach decisions
- Enable opt-out mechanisms where automated processing occurs
- Conduct algorithmic impact assessments evaluating bias and discrimination risks
In addition, training machine learning models on personal data requires careful attention to data minimisation, purpose limitation, and retention principles. Therefore, implementing federated learning or differential privacy techniques may become necessary for certain AI applications.
Quantum Computing and Cryptographic Resilience
AWS's quantum computing service Braket highlights an emerging threat to current encryption standards. Furthermore, GDPR's requirement for security measures considering "the state of the art" necessitates planning for post-quantum cryptography:
- Monitor NIST's post-quantum standardisation process and AWS's implementation timeline
- Inventory cryptographic dependencies across AWS services and applications
- Plan migration pathways to quantum-resistant algorithms
- Consider crypto-agility in architecture designs enabling algorithm updates
Nevertheless, practical quantum threats to encryption remain years away for most organisations. Therefore, maintaining current best practices whilst monitoring developments provides appropriate risk management.
Regulatory Harmonisation and Global Privacy Laws
GDPR's influence extends globally, with similar frameworks emerging in Brazil (LGPD), California (CCPA/CPRA), and other jurisdictions. Moreover, AWS's global infrastructure enables multi-jurisdictional compliance, yet organisations must navigate varying requirements:
| Regulation | Jurisdiction | Key Differences from GDPR |
|---|---|---|
| LGPD | Brazil | Similar principles, different supervisory structure |
| CCPA/CPRA | California | Broader definition of personal information, different rights framework |
| PIPA | South Korea | Stricter consent requirements, different breach thresholds |
| PDPA | Singapore | Accountability-based, different transfer mechanisms |
Furthermore, implementing compliance frameworks addressing multiple regulations simultaneously reduces redundant effort. Therefore, frameworks like NIST's Privacy Framework help map GDPR requirements to technical controls applicable across jurisdictions.
Implementing robust GDPR compliance on AWS requires careful attention to shared responsibilities, technical controls, and ongoing accountability measures. Nevertheless, organisations seeking simplified compliance with guaranteed European data residency may find dedicated European cloud providers offer clearer regulatory alignment. vBoxx operates ISO 27001-certified infrastructure exclusively within the Netherlands, eliminating international transfer complexities whilst providing enterprise cloud storage, communication platforms, and security tools designed specifically for European privacy requirements. For businesses prioritising GDPR compliance without navigating complex multi-jurisdictional frameworks, exploring European alternatives ensures data sovereignty and regulatory certainty from the ground up.