
The landscape of enterprise computing has transformed dramatically over the past decade, with cloud based servers for business emerging as the backbone of modern digital operations. Organisations of all sizes are transitioning from traditional on-premises infrastructure to cloud-hosted environments, driven by the need for greater flexibility, improved disaster recovery capabilities, and reduced capital expenditure. Furthermore, the shift towards remote and hybrid working models has accelerated cloud adoption, making it essential for businesses to understand the full spectrum of cloud server options available. This comprehensive guide examines the critical considerations, deployment models, security frameworks, and cost optimisation strategies that define successful cloud server implementations in 2026.
Understanding Cloud Server Architecture and Deployment Models
Cloud based servers for business operate on virtualised infrastructure, allowing multiple virtual machines to run on shared physical hardware whilst maintaining isolation and security. The National Institute of Standards and Technology (NIST) defines cloud computing through five essential characteristics: on-demand self-service, broad network access, resource pooling, rapid elasticity, and measured service. These characteristics fundamentally distinguish cloud servers from traditional hosting arrangements.
Public, Private, and Hybrid Cloud Considerations
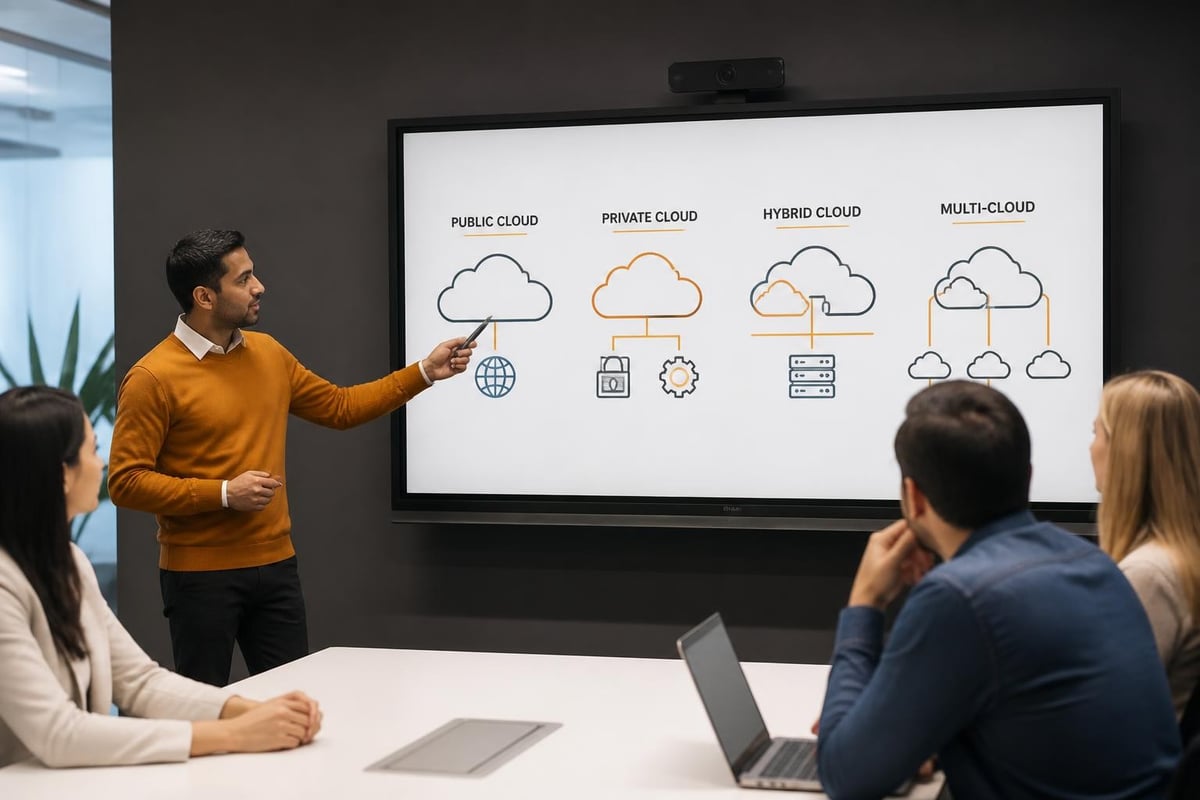
Businesses typically choose from three primary deployment models, each offering distinct advantages. Public cloud environments provide shared infrastructure managed by third-party providers, delivering excellent scalability and cost efficiency for standard workloads. Private cloud deployments, in contrast, dedicate infrastructure to a single organisation, offering enhanced control over security policies and compliance requirements. Hybrid cloud architectures combine both approaches, enabling organisations to keep sensitive data on private infrastructure whilst leveraging public cloud resources for development, testing, or burst capacity.
The selection between these models depends heavily on regulatory requirements and data sovereignty concerns. For European businesses, the location of cloud infrastructure carries particular significance due to GDPR obligations and the extraterritorial reach of foreign legislation. Moreover, hybrid approaches allow organisations to maintain compliance-sensitive workloads within European data centres whilst utilising global cloud resources for less-regulated operations.
| Deployment Model | Best Use Cases | Primary Advantages | Key Considerations |
|---|---|---|---|
| Public Cloud | Development, testing, standard applications | Cost efficiency, rapid deployment, unlimited scale | Data sovereignty, shared security responsibility |
| Private Cloud | Regulated industries, sensitive data, legacy applications | Full control, dedicated resources, customisation | Higher costs, maintenance overhead |
| Hybrid Cloud | Mixed workloads, cloud migration, disaster recovery | Flexibility, gradual migration, balanced costs | Complex management, integration challenges |
Service Models: Infrastructure, Platform, and Software
Cloud based servers for business are delivered through three primary service models, each abstracting different layers of the technology stack. Infrastructure as a Service (IaaS) provides virtualised computing resources over the internet, giving businesses control over operating systems, storage, and deployed applications. Platform as a Service (PaaS) adds another abstraction layer, managing the underlying infrastructure whilst providing development frameworks and middleware. Software as a Service (SaaS) delivers complete applications through the cloud, eliminating infrastructure management entirely.
Choosing the Right Service Model for Your Workloads
Most organisations adopt a multi-layered approach, selecting different service models for different business functions. IaaS proves ideal for organisations requiring maximum control over their server environment, particularly when migrating legacy applications or maintaining specific configurations. Consequently, businesses with highly customised software stacks or strict compliance requirements frequently prefer IaaS deployments.
PaaS accelerates application development by providing pre-configured environments, databases, and development tools. Development teams benefit from reduced setup time and standardised deployment pipelines. Nevertheless, PaaS introduces vendor lock-in risks, as applications may become dependent on proprietary platform features and APIs.
- IaaS strengths: Full control, custom configurations, support for legacy systems, flexible networking
- PaaS strengths: Rapid development, automatic scaling, integrated DevOps tools, reduced management overhead
- SaaS strengths: Zero infrastructure management, predictable costs, automatic updates, immediate deployment
Security and Compliance in Cloud Server Environments
Security remains the paramount concern when evaluating cloud based servers for business applications. The shared responsibility model defines the division of security obligations between cloud providers and customers. Providers typically secure the underlying infrastructure, physical facilities, and virtualisation layers, whilst customers remain responsible for securing their data, applications, access controls, and network configurations.
Furthermore, the AWS Security Best Practices framework outlines essential controls including identity and access management, network segmentation, encryption at rest and in transit, logging and monitoring, and incident response procedures. These principles apply broadly across cloud platforms, providing a foundation for robust security architectures.
GDPR Compliance and Data Sovereignty
European businesses must navigate complex data protection requirements when selecting cloud infrastructure. The General Data Protection Regulation imposes strict controls on personal data processing, including requirements for data localisation, processor agreements, and cross-border transfer mechanisms. Therefore, the European Data Protection Board guidance on cloud services emphasises the importance of contractual safeguards, technical measures, and careful vendor selection.
Businesses subject to GDPR must ensure their cloud providers offer:
- Data residency guarantees within the European Economic Area
- Comprehensive data processing agreements aligned with Article 28 requirements
- Technical and organisational measures demonstrating appropriate security levels
- Transparent subprocessor relationships and notification procedures
- Support for data subject rights including access, deletion, and portability
The location of cloud infrastructure directly impacts legal jurisdiction and data access rights. European providers operating infrastructure within EU borders offer stronger protection against extraterritorial data access requests. Additionally, choosing providers outside the scope of foreign legislation such as the US CLOUD Act provides enhanced data sovereignty and control.
Implementing Zero-Trust Architecture
Modern cloud security increasingly adopts zero-trust principles, assuming no implicit trust based on network location. This approach requires explicit verification for every access request, implementing least-privilege access controls, and continuous monitoring of user and device behaviour. Consequently, zero-trust architectures significantly reduce the attack surface and limit potential breach impacts.
Implementation begins with strong identity and access management, deploying multi-factor authentication across all user accounts and service connections. Network segmentation using virtual private clouds and security groups ensures workloads operate in isolated environments. Moreover, the CIS Benchmarks provide detailed configuration guidance for hardening cloud server instances and associated services.
Cost Optimisation and Financial Operations
The economic advantages of cloud based servers for business extend beyond reduced capital expenditure. However, unmanaged cloud consumption frequently leads to unexpected costs and inefficient resource utilisation. Financial Operations (FinOps) has emerged as a crucial discipline, combining financial accountability, operational efficiency, and cross-functional collaboration to maximise cloud business value.
The FinOps Foundation defines FinOps as a cultural practice bringing together finance, technology, and business teams to make informed spending decisions. This framework enables organisations to understand cloud costs, allocate expenses accurately, and continuously optimise resource consumption. Furthermore, FinOps promotes accountability by linking cloud spending directly to business outcomes and team budgets.
Practical Cost Control Strategies
Effective cost management begins with comprehensive visibility into cloud resource consumption. Tagging strategies allow organisations to categorise resources by department, project, environment, or cost centre, enabling detailed cost allocation and chargeback mechanisms. Subsequently, teams can identify wasteful spending patterns and optimise their resource footprint.
Microsoft’s guidance on workload optimisation emphasises rightsizing as a primary cost reduction lever. Many organisations overprovision cloud servers, purchasing instance types with excessive CPU, memory, or storage capacity. Regular analysis of actual resource utilisation reveals opportunities to downsize instances or migrate to more cost-effective instance families.
| Cost Optimisation Tactic | Potential Savings | Implementation Complexity | Best For |
|---|---|---|---|
| Reserved instances/committed use | 30-70% reduction | Low | Predictable workloads |
| Rightsizing instances | 15-40% reduction | Medium | Over-provisioned resources |
| Automated start/stop schedules | 40-65% reduction | Low | Development/test environments |
| Spot/preemptible instances | 60-90% reduction | High | Fault-tolerant workloads |
Additional optimisation opportunities include implementing automated shutdown schedules for non-production environments, leveraging spot instances for flexible workloads, and consolidating underutilised servers. Moreover, Google Cloud’s FinOps guide recommends establishing regular cost review cadences and setting up budget alerts to prevent unexpected spending spikes.
Performance Optimisation and Workload Management
Cloud based servers for business must deliver consistent performance whilst efficiently utilising allocated resources. Performance optimisation requires understanding workload characteristics, selecting appropriate instance types, and implementing effective monitoring and auto-scaling policies. Nevertheless, achieving optimal performance involves balancing competing priorities including cost, reliability, and response time.
Instance Selection and Configuration
Modern cloud providers offer extensive instance type portfolios, optimised for different workload patterns. Compute-optimised instances provide high CPU-to-memory ratios for processor-intensive applications, whilst memory-optimised instances suit databases and in-memory analytics. Storage-optimised instances deliver high sequential read and write access for data warehousing and log processing workloads.
Beyond basic instance selection, configuration choices significantly impact performance. Network-optimised instances provide enhanced throughput and lower latency for distributed applications and microservices architectures. Businesses running demanding workloads increasingly leverage instances with dedicated CPU cores, avoiding performance variability from shared virtualisation overhead.
- Select instance families matching workload characteristics (compute, memory, storage, or network intensive)
- Enable enhanced networking for latency-sensitive applications
- Use local SSD storage for temporary high-IOPS requirements
- Implement connection pooling and caching to reduce database load
- Deploy content delivery networks for geographically distributed users
Implementing Effective Auto-Scaling
Auto-scaling capabilities distinguish cloud based servers for business from traditional infrastructure, automatically adjusting capacity to match demand. Horizontal scaling adds or removes server instances based on predefined metrics such as CPU utilisation, memory consumption, or request queue length. Vertical scaling modifies instance specifications, though this approach typically requires brief downtime.
Effective auto-scaling policies require careful metric selection and threshold configuration. Aggressive scaling policies respond quickly to demand spikes but may trigger unnecessary scaling events due to temporary fluctuations. Conservative policies reduce costs but risk performance degradation during genuine demand increases. Therefore, businesses should analyse historical traffic patterns and gradually tune scaling parameters based on observed behaviour.
Migration Strategies and Change Management
Transitioning to cloud based servers for business represents a significant organisational change, extending beyond technical migration to encompass process redesign, skills development, and cultural adaptation. The AWS Cloud Adoption Framework provides structured guidance across six perspectives: business, people, governance, platform, security, and operations.
Planning Your Migration Journey
Successful migrations begin with comprehensive application discovery and dependency mapping. Understanding which applications communicate with each other, their performance requirements, and compliance constraints enables informed decisions about migration priorities and approaches. Furthermore, businesses should categorise applications using the six Rs framework: rehost (lift and shift), replatform (lift and reshape), repurchase (replace with SaaS), refactor (re-architect), retire, or retain.
Rehosting provides the fastest migration path, moving applications to cloud servers with minimal modifications. This approach suits organisations seeking rapid data centre exits or immediate cost reductions. However, rehosted applications typically fail to leverage cloud-native capabilities such as auto-scaling, managed services, or serverless architectures.
Replatforming strikes a balance between speed and optimisation, making targeted updates to leverage cloud services without complete redesign. Applications might migrate from self-managed databases to managed database services, or from static server fleets to auto-scaling groups. Consequently, replatforming delivers tangible benefits whilst controlling migration complexity and risk.
- Conduct application discovery and dependency mapping
- Assess technical feasibility and business value for each workload
- Categorise applications using the six Rs framework
- Develop detailed migration plans with rollback procedures
- Execute pilot migrations with non-critical applications
- Establish cloud centre of excellence for ongoing optimisation
Disaster Recovery and Business Continuity
Cloud based servers for business fundamentally enhance disaster recovery capabilities through geographic distribution, automated backup services, and rapid provisioning. Traditional disaster recovery approaches required duplicate physical infrastructure, resulting in substantial capital investment for rarely used capacity. Cloud environments enable cost-effective recovery strategies through on-demand resource provisioning and pay-per-use pricing models.
Defining Recovery Objectives
Business continuity planning begins with establishing Recovery Time Objectives (RTO) and Recovery Point Objectives (RPO) for each application. RTO defines the maximum acceptable downtime following a disaster, whilst RPO specifies the maximum data loss tolerance. These metrics drive architectural decisions and investment levels for backup and redundancy systems.
Mission-critical applications with stringent RTO and RPO requirements typically employ active-active architectures, simultaneously operating across multiple geographic regions. Database replication ensures data consistency across regions, whilst global load balancing directs traffic to healthy instances. Although this approach maximises availability, it substantially increases operational costs and complexity.
Less critical applications may utilise warm standby or backup and restore strategies. Warm standby maintains scaled-down capacity in a secondary region, ready for rapid expansion during failures. Backup and restore periodically snapshots data and configuration, accepting longer recovery times in exchange for minimal standby costs. Therefore, organisations should align disaster recovery investment with actual business impact and recovery requirements.
Monitoring, Logging, and Observability
Effective management of cloud based servers for business demands comprehensive monitoring and logging infrastructure. Observability extends beyond traditional monitoring, providing deep insight into system behaviour through metrics, logs, and distributed traces. This holistic view enables rapid troubleshooting, capacity planning, and security incident detection.
Building Monitoring Infrastructure
Cloud monitoring strategies typically combine provider-native tools with third-party platforms offering cross-cloud visibility and advanced analytics. Native monitoring services integrate seamlessly with cloud infrastructure, providing detailed metrics for compute instances, databases, storage, and network resources. Nevertheless, organisations operating multi-cloud or hybrid environments benefit from unified monitoring platforms aggregating data across all infrastructure components.
Effective monitoring requires establishing meaningful baselines for normal operation, enabling automated detection of anomalies and performance degradation. Alert fatigue remains a persistent challenge, as overly sensitive alerting overwhelms operations teams with false positives. Moreover, well-designed alert policies distinguish between informational events, warnings requiring investigation, and critical incidents demanding immediate response.
For European businesses requiring GDPR-compliant analytics and monitoring, platforms like vBoxx Analytics provide detailed insights whilst maintaining data sovereignty and privacy controls. Such solutions ensure monitoring data remains within European jurisdiction, addressing compliance requirements whilst delivering operational visibility.
| Monitoring Category | Key Metrics | Collection Frequency | Retention Period |
|---|---|---|---|
| Infrastructure | CPU, memory, disk, network utilisation | 1-5 minutes | 30-90 days |
| Application | Response time, error rate, throughput | Real-time | 30-365 days |
| Security | Failed logins, privilege escalations, unusual access | Real-time | 365+ days |
| Cost | Resource consumption, spend by service/tag | Daily | 12+ months |
Vendor Selection and Multi-Cloud Strategy
Selecting cloud providers for business-critical servers requires evaluating technical capabilities, geographic coverage, compliance certifications, and commercial terms. The IDC analysis of cloud market trends reveals increasing enterprise adoption of multi-cloud strategies, distributing workloads across multiple providers to avoid vendor lock-in, optimise costs, and enhance resilience.
Evaluating Provider Capabilities
Technical evaluation should encompass compute instance variety, storage performance and durability, networking capabilities, managed service portfolio, and API maturity. Geographic presence directly impacts latency for end users and compliance with data residency requirements. European businesses particularly benefit from providers operating infrastructure within EU borders, ensuring GDPR compliance and protection from extraterritorial legislation.
Compliance certifications demonstrate provider commitment to security and operational standards. ISO 27001 certification validates information security management systems, whilst SOC 2 reports provide detailed controls evidence. Industry-specific certifications such as PCI DSS for payment processing or HIPAA for healthcare data may be mandatory depending on business operations.
For organisations requiring European infrastructure with strong privacy protections, providers like vBoxx operate ISO 27001-certified data centres in the Netherlands, offering virtual and dedicated servers alongside complementary cloud services. Furthermore, European providers outside US jurisdiction provide enhanced data sovereignty, particularly valuable for businesses handling sensitive personal or commercial data.
Managing Multi-Cloud Complexity
Multi-cloud architectures introduce significant operational complexity, requiring teams to master multiple management interfaces, APIs, and service portfolios. Standardisation through infrastructure-as-code templates and configuration management tools helps maintain consistency across environments. Nevertheless, achieving true cloud portability remains challenging due to provider-specific services and architectural patterns.
Organisations should approach multi-cloud strategically, avoiding unnecessary complexity from distributing individual applications across providers. More practical approaches include dedicating specific workload types to particular clouds based on their strengths, or maintaining secondary cloud environments for disaster recovery purposes. Additionally, maintaining expertise across multiple platforms requires substantial training investment and specialised hiring.
Cloud based servers for business have fundamentally transformed how organisations deploy, scale, and manage their digital infrastructure, offering unprecedented flexibility and economic efficiency. Success requires careful attention to security, compliance, cost optimisation, and operational excellence throughout the cloud journey. Whether you need GDPR-compliant virtual servers, managed hosting solutions, or comprehensive cloud infrastructure, vBoxx delivers secure, European-hosted services from ISO 27001-certified data centres in the Netherlands, combining technical excellence with strong privacy protections and sustainable hosting practices.