
Modern businesses face an escalating threat landscape where cyberattacks grow more sophisticated every month. Consequently, organisations across Europe are turning to specialist Security Operations Centre (SOC) providers to monitor their digital infrastructure around the clock. These managed security service providers deliver expert threat detection, incident response, and continuous monitoring capabilities that many in-house teams struggle to maintain. Furthermore, as regulatory requirements tighten and the skills gap in cybersecurity widens, the decision to partner with external soc providers has become a strategic imperative for enterprises of all sizes.
Understanding the Core Functions of SOC Providers
SOC providers deliver centralised security monitoring and incident response services that protect organisations from cyber threats. Moreover, these specialists operate 24/7/365 facilities staffed by trained analysts who monitor security events, investigate anomalies, and coordinate responses to confirmed incidents.
At their foundation, soc providers aggregate log data and security telemetry from across a client's IT estate. Therefore, they can correlate events from firewalls, endpoints, cloud services, network devices, and applications into a unified view of the security posture. This holistic visibility enables detection of attack patterns that would remain invisible when examining individual systems in isolation.
The UK National Cyber Security Centre provides comprehensive guidance on the essential components and operating models for both in-house and outsourced security operations centres, highlighting the importance of well-defined processes and appropriate tooling.
Key Service Components
Professional soc providers typically deliver several integrated capabilities:
- Continuous monitoring of security events across all monitored systems
- Threat detection using signature-based, behavioural, and anomaly-detection methods
- Incident triage and investigation to determine the scope and severity of alerts
- Incident response coordination including containment, eradication, and recovery activities
- Threat intelligence integration to identify emerging attack techniques and indicators of compromise
- Compliance reporting aligned to frameworks such as GDPR, ISO 27001, and NIS2
In addition, many providers offer vulnerability management, security awareness training, and strategic advisory services as complementary offerings. Nevertheless, the core value proposition remains constant: expert eyes on your security posture when your internal team cannot maintain round-the-clock coverage.
Selecting the Right SOC Provider for European Businesses
Choosing an appropriate SOC partner requires careful evaluation of both technical capabilities and strategic alignment. Furthermore, European organisations must consider specific regulatory and jurisdictional factors that influence provider selection.
Technical Capability Assessment
When evaluating soc providers, organisations should examine several technical dimensions to ensure the provider can deliver effective protection:
| Evaluation Criterion | Key Considerations | Why It Matters |
|---|---|---|
| Detection Coverage | Number of use cases, threat signatures, behavioral analytics, MITRE ATT&CK alignment | Determines breadth of threats the SOC can identify |
| Response Times | Mean time to detect (MTTD), mean time to respond (MTTR), SLA commitments | Directly impacts damage limitation during incidents |
| Technology Stack | SIEM platform, EDR tools, threat intelligence feeds, automation capabilities | Affects detection accuracy and operational efficiency |
| Analyst Expertise | Certifications, experience levels, specialization areas, retention rates | Determines quality of investigation and response guidance |
| Integration Flexibility | API support, log source compatibility, cloud platform coverage | Ensures the SOC can monitor your specific environment |
The SANS 2023 SOC Survey provides valuable empirical data on the challenges facing SOC teams and the tool satisfaction levels that correlate with effective security operations. Therefore, prospective clients should ask providers about their participation in industry benchmarking studies and how their performance compares to peer organisations.
Regulatory and Data Sovereignty Considerations
European businesses operating under GDPR face unique requirements when selecting soc providers. In particular, the location of security data processing and storage carries significant legal implications.
Organisations must verify that their SOC provider processes and stores security telemetry within the European Economic Area. Moreover, they should confirm that the provider operates outside the jurisdiction of extraterritorial data access laws such as the US CLOUD Act, which can compel US-based companies to disclose customer data regardless of storage location.
Additionally, contracts should clearly define data handling procedures, retention periods, and the provider's obligations regarding data subject access requests and breach notifications. Nevertheless, many organisations overlook these details during initial procurement, creating compliance gaps that surface only during audits or incidents.
Operational Integration and Effectiveness Metrics
Successfully partnering with soc providers requires more than simply signing a contract and forwarding log files. Furthermore, organisations must establish clear communication channels, escalation procedures, and performance measurement frameworks to ensure the relationship delivers value.
Establishing Effective SOC Integration
The onboarding phase sets the foundation for long-term success. Therefore, organisations should invest time in several critical activities:
- Asset inventory and prioritisation to ensure the SOC monitors your most critical systems
- Use case development aligned to your specific threat landscape and compliance requirements
- Escalation pathway definition clarifying when and how the SOC contacts internal teams
- Playbook customisation adapting standard response procedures to your environment and risk tolerance
- Communication protocol establishment defining reporting frequency, formats, and stakeholder distribution
In addition, organisations should designate an internal point of contact who maintains regular dialogue with the SOC provider. This relationship manager ensures that the provider remains informed about infrastructure changes, planned maintenance windows, and evolving business priorities that may affect security monitoring requirements.
The MITRE ATT&CK framework provides essential resources for developing threat-informed detection use cases that align SOC monitoring to real-world adversary techniques. Consequently, organisations should work with their soc providers to map detection coverage across the ATT&CK matrix and identify gaps in visibility.
Measuring SOC Provider Performance
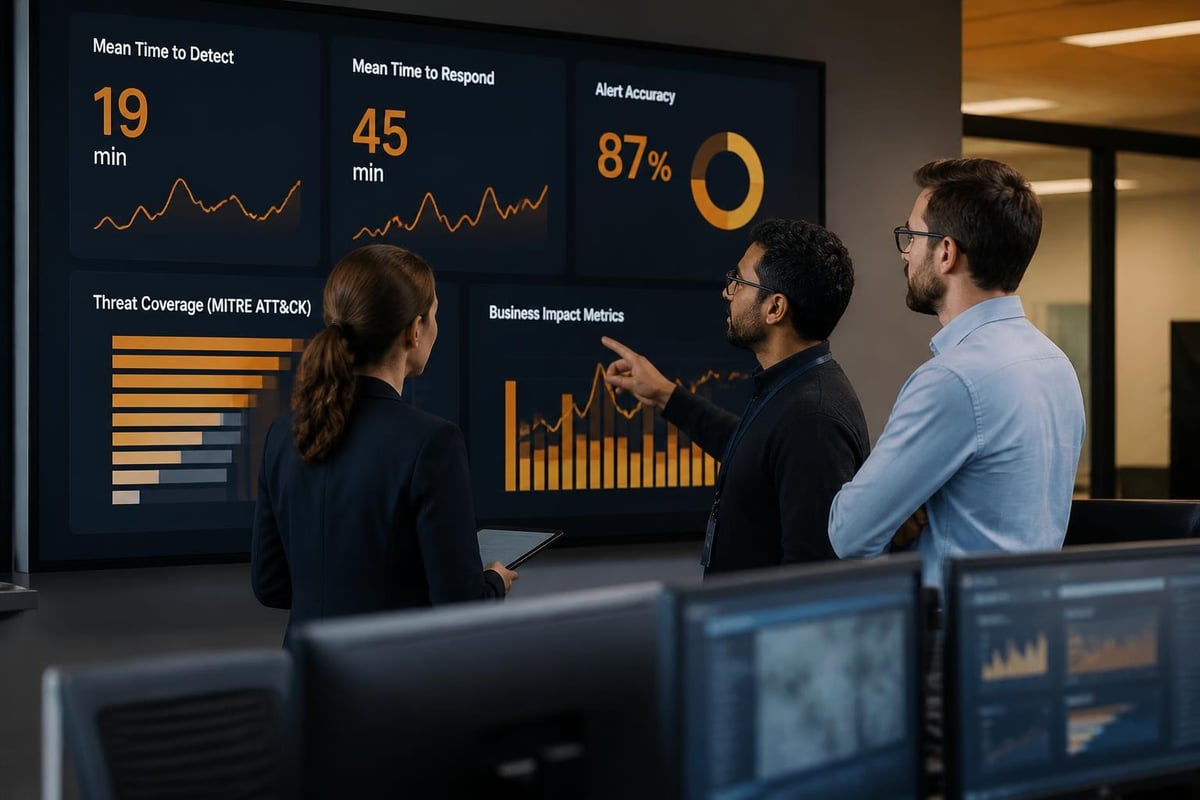
Effective measurement requires both technical and business-oriented metrics. Moreover, organisations should establish baseline performance levels during the first quarter of engagement and track improvement over time.
The SANS SOC Metrics Cheat Sheet offers practical guidance on selecting meaningful key performance indicators that demonstrate SOC effectiveness. Nevertheless, organisations should customise these metrics to reflect their specific risk profile and operational context.
Technical performance metrics include:
- Mean time to detect (MTTD) for different threat categories
- Mean time to respond (MTTR) from initial alert to containment
- Alert volume and false positive rates
- Escalation accuracy (percentage of escalated incidents confirmed as genuine threats)
- Coverage percentage across the MITRE ATT&CK framework
Business value metrics encompass:
- Number of prevented security incidents
- Cost avoidance from early threat detection
- Compliance audit findings related to security monitoring
- Reduction in security-related business disruption
- Internal team time freed from alert triage
Furthermore, quarterly business reviews should examine these metrics alongside emerging threats, infrastructure changes, and lessons learned from recent incidents. Therefore, the relationship evolves from a transactional service arrangement into a strategic partnership focused on continuous improvement.
Cost Models and Commercial Considerations
Pricing structures for soc providers vary considerably based on service scope, monitoring volume, and contractual commitments. Moreover, understanding the underlying cost drivers helps organisations negotiate fair agreements and avoid unexpected expenses.
Common Pricing Approaches
Most soc providers employ one of several standard pricing models:
- Per-device pricing charges a monthly fee for each monitored endpoint, server, or network device
- Per-log-volume pricing bases costs on the quantity of log data ingested and analyzed
- User-based pricing calculates fees according to the number of employees or licensed users
- Tiered service packages offer predefined bundles combining monitoring scope with response capabilities
- Hybrid models combine base platform fees with usage-based components
In addition, organisations should clarify which activities fall within standard service fees versus those that trigger additional charges. For instance, some providers include basic incident investigation but charge separately for extended forensic analysis, threat hunting sprints, or on-site incident response support.
Hidden Costs and Budget Planning
Beyond the headline service fee, organisations should budget for several associated expenses. Nevertheless, many procurement processes focus exclusively on the monthly SOC charge whilst overlooking these complementary costs:
- Integration and onboarding efforts requiring internal IT resources
- Log forwarding infrastructure such as log collectors, network bandwidth, and storage
- Compliance or regulatory reporting requiring custom report development
- Remediation activities following incident detection
- Internal security team coordination time spent managing the provider relationship
Therefore, a comprehensive total cost of ownership calculation should include both direct provider fees and these internal resource commitments. Furthermore, organisations should negotiate clear statements of work that define the boundary between provider responsibilities and client obligations.
Cloud-Era Challenges for SOC Providers
The migration to cloud infrastructure fundamentally changes the security monitoring landscape. Consequently, soc providers must adapt their technology stacks, detection methodologies, and operational processes to maintain effectiveness across hybrid and multi-cloud environments.
Multi-Cloud Visibility Complexity
Modern enterprises typically operate workloads across multiple cloud platforms alongside traditional on-premises infrastructure. Moreover, each cloud provider offers distinct logging mechanisms, security controls, and monitoring APIs that complicate unified threat detection.
Effective soc providers demonstrate capability across major cloud platforms:
| Cloud Platform | Key Monitoring Challenges | Provider Capabilities to Verify |
|---|---|---|
| AWS | CloudTrail volume, multi-account architectures, ephemeral compute | GuardDuty integration, CloudWatch analysis, VPC flow log correlation |
| Microsoft Azure | Activity log complexity, hybrid identity, multi-subscription sprawl | Sentinel connector deployment, Entra ID monitoring, Azure Arc coverage |
| Google Cloud | Audit log configuration, GKE container visibility, project isolation | Chronicle integration, GKE security posture monitoring, VPC flow analysis |
In addition, organisations adopting cloud-native services such as serverless computing, managed databases, and container orchestration platforms must verify that their SOC provider can monitor these environments effectively. Nevertheless, many traditional soc providers struggle with cloud workload visibility, particularly in containerized and serverless architectures where traditional agent deployment proves challenging.
The ISACA guidance on elevating SOC capabilities emphasizes the importance of cloud-era detection strategies and the need to evolve SOC operating models alongside infrastructure modernization efforts.
Identity-Centric Threat Detection
Cloud environments shift the security perimeter from network boundaries to identity and access management. Therefore, effective cloud monitoring requires strong visibility into authentication events, privilege escalation attempts, and anomalous access patterns.
Furthermore, soc providers must correlate identity activity across multiple systems to detect sophisticated attack chains. For example, an adversary might compromise a low-privilege account, perform reconnaissance through legitimate cloud management APIs, escalate privileges using misconfigured IAM policies, and exfiltrate data through sanctioned cloud storage services. Each individual action appears benign, but the sequence reveals malicious intent.
Organisations should verify that their SOC provider monitors:
- Multi-factor authentication bypass attempts
- Privilege escalation through cloud IAM
- Lateral movement between cloud resources
- Data access by unusual user accounts or locations
- API abuse and automation tool misuse
Moreover, integration with cloud-native security services such as AWS GuardDuty, Microsoft Sentinel, and Google Chronicle can enhance detection capabilities whilst reducing log ingestion costs.
Regulatory Compliance and SOC Provider Selection
European regulatory frameworks increasingly mandate specific security monitoring capabilities. Consequently, organisations must ensure their chosen soc providers support compliance requirements across applicable regulations.
GDPR and Privacy Considerations
The General Data Protection Regulation creates specific obligations regarding security monitoring and incident response. Furthermore, organisations remain liable for data protection compliance even when outsourcing security operations to third-party providers.
When evaluating soc providers, European organisations should verify several GDPR-related capabilities. Therefore, request evidence of:
- Data processing agreements (DPAs) that clearly define roles and responsibilities
- Subprocessor disclosure for any tools or services the SOC uses
- Data residency commitments ensuring security telemetry remains within the EEA
- Breach notification procedures aligned to the 72-hour GDPR requirement
- Data retention and deletion processes for security logs containing personal data
In addition, organisations should consider the jurisdictional exposure created by their SOC provider's corporate structure. Nevertheless, providers headquartered in or controlled by entities in jurisdictions with expansive data access laws may face conflicting legal obligations during security investigations involving European customer data.
For businesses requiring robust data sovereignty guarantees, partnering with European-headquartered providers operating infrastructure within the EEA offers the strongest compliance posture. Moreover, services such as vBoxxCloud demonstrate how European providers emphasize GDPR compliance and exemption from extraterritorial data access regimes as core value propositions.
NIS2 Directive Requirements
The revised Network and Information Security Directive (NIS2) expands security obligations across essential and important entities throughout the European Union. Furthermore, the directive specifically mandates incident detection, response, and reporting capabilities that many organisations will fulfill through partnerships with soc providers.
NIS2-covered entities should verify that their SOC provider supports:
- Incident detection and monitoring across all systems processing essential services
- Incident classification according to severity and impact thresholds
- Regulatory notification support including timeline tracking and evidence gathering
- Supply chain risk management including monitoring of critical supplier connections
- Cybersecurity governance reporting to support board-level oversight
Therefore, contracts should explicitly reference NIS2 compliance obligations and define how the SOC provider will support regulatory reporting requirements. Nevertheless, organisations must remember that outsourcing monitoring does not transfer regulatory accountability. Senior management remains personally liable for security failures under NIS2's executive accountability provisions.
Building Effective SOC Provider Relationships
Long-term success requires treating the SOC provider as a strategic partner rather than a commodity vendor. Moreover, organisations that invest in relationship development typically achieve superior security outcomes compared to those maintaining purely transactional arrangements.
Continuous Improvement Frameworks
The most effective SOC engagements incorporate structured improvement processes. Furthermore, regular assessment of detection capabilities, response effectiveness, and emerging threats ensures the service evolves alongside the threat landscape.
Quarterly improvement cycles should include:
- Threat landscape reviews examining new attack techniques relevant to your industry
- Use case gap analysis identifying detection blind spots in current monitoring coverage
- False positive reduction sprints refining detection logic to improve alert accuracy
- Playbook optimization updating response procedures based on lessons learned
- Technology roadmap alignment planning for infrastructure changes that affect monitoring
In addition, organisations should participate in threat intelligence sharing communities relevant to their sector. Therefore, insights from Information Sharing and Analysis Centres (ISACs) can inform SOC detection priorities and help providers anticipate emerging threats before they manifest in your environment.
The NIST guidance on cyber threat information sharing provides authoritative standards for establishing information exchange processes with SOC providers and peer organisations.
Incident Response Collaboration
The true test of a SOC provider relationship occurs during actual security incidents. Nevertheless, organisations often discover gaps in escalation procedures, decision authority, and technical integration only when responding to real threats under time pressure.
Consequently, regular tabletop exercises and simulated incidents build muscle memory across both provider and client teams. These exercises should test:
- Alert escalation pathways and notification procedures
- Decision-making authority for containment actions
- Evidence preservation and forensic investigation workflows
- Communication protocols with executive leadership and external stakeholders
- Recovery coordination between the SOC and internal IT operations
Moreover, post-incident reviews should examine both technical response effectiveness and process efficiency. Therefore, each incident becomes a learning opportunity that strengthens future response capabilities.
Recent guidance from CISA on monitoring recommendations highlights specific detection and response improvements that SOC teams should implement based on observed adversary techniques. Furthermore, organisations should work with their soc providers to incorporate these recommendations into their monitoring posture.
Vendor Evaluation and Procurement Process
Selecting the optimal SOC provider requires a structured evaluation process that balances technical capabilities, commercial terms, and strategic fit. Moreover, organisations should resist the temptation to award contracts based solely on pricing or incumbent relationships.
Request for Proposal Development
A well-constructed RFP enables meaningful comparison across providers whilst communicating your specific requirements. Furthermore, the RFP process helps organisations clarify their own security priorities and service expectations before committing to a multi-year engagement.
Effective RFPs should address:
- Current environment description including infrastructure inventory, existing security tools, and compliance requirements
- Service scope definition specifying systems to monitor, response expectations, and reporting needs
- Technical requirements detailing integration methods, log sources, and coverage expectations
- Performance standards establishing SLAs for detection, response, and availability
- Commercial parameters outlining contract duration, pricing models, and growth assumptions
In addition, request evidence of provider capabilities rather than relying on marketing claims. Therefore, ask for customer references in your industry, SOC2 or ISO 27001 certification evidence, and anonymized metrics demonstrating historical performance.
Proof of Concept Considerations
For significant SOC engagements, a limited proof of concept can validate provider capabilities before full commitment. Nevertheless, PoC scopes should be carefully defined to test critical capabilities without creating excessive evaluation overhead.
Effective PoC scenarios typically focus on:
- Detection accuracy for threats relevant to your environment
- Integration with your specific infrastructure and security tools
- Quality of analyst investigations and escalation communications
- Reporting clarity and business value articulation
- Responsiveness to questions and collaboration effectiveness
Moreover, evaluate not just technical performance but also the provider's partnership approach during the PoC period. Therefore, providers who demonstrate consultative engagement, proactive recommendations, and transparent communication during evaluation typically maintain these behaviors through long-term relationships.
Industry analyst frameworks such as Forrester’s security service evaluations provide vendor-selection criteria and market differentiation insights that inform procurement decisions.
Selecting and managing soc providers requires balancing technical capability, regulatory compliance, and strategic partnership across an evolving threat landscape. European businesses particularly benefit from providers who combine security expertise with GDPR compliance, data sovereignty guarantees, and alignment to regional regulatory frameworks. As organisations build resilient security operations, partnering with infrastructure providers who prioritize European data sovereignty creates a strong foundation for compliance and protection. vBoxx delivers ISO 27001-certified infrastructure in the Netherlands, supporting secure hosting, cloud storage, communication platforms, and backup services outside the reach of extraterritorial data access laws. Explore how European-based infrastructure can strengthen your security and compliance posture today.